Executive Overview
The open-source software ecosystem is facing an unprecedented operational crisis. For decades, the foundational infrastructure powering the modern internet has relied on the goodwill, patience, and tireless labor of human maintainers. Today, however, that human-centric model is buckling under the weight of generative artificial intelligence.
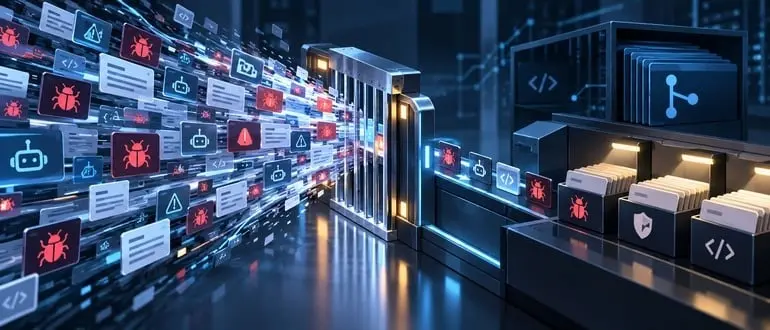
AI-driven security tools, automated vulnerability scanners, and large language models (LLMs) are generating software bug reports at an exponential, industrial scale. While these technologies have democratized the discovery of potential software flaws, they have simultaneously birthed a catastrophic signal-to-noise ratio. Open-source maintainers are drowning in a sea of low-quality, ambiguous, and bulk-generated security submissions.
In response to this systemic breakdown, GitHub has introduced a radical countermeasure: daily rate limits on new private vulnerability reports, coupled with structured reporting forms. This decisive intervention represents a profound structural admission by the world’s largest code host. The traditional security-disclosure workflow—built on the assumption that human judgment is an abundant, infinitely scalable resource—no longer functions.
The scarce resource in modern cybersecurity is no longer the discovery of a potential flaw; it is the informed human judgment required to triage, verify, and remediate it. By capping the velocity of incoming disclosures and standardizing the intake pipeline, GitHub is attempting to buy open-source projects breathing room. Yet, these measures raise pressing questions about how the developer community will balance security automation against the administrative friction imposed on legitimate human researchers.
Detailed Chronology: The Evolution of the Intake Crisis
The implementation of rate limits and structured reporting forms on October 1, 2026, did not happen in a vacuum. It was the culmination of years of escalating tension between automated vulnerability generation and human triage capacity.
The Rise of Automated Disclosures
As AI code assistants and automated fuzzing engines matured through the mid-2020s, security researchers and malicious actors alike gained the ability to rapidly scan vast codebases for anomalies. Initially, this was celebrated as a triumph for proactive defense. However, the commercialization and democratization of LLMs unleashed a torrent of speculative, poorly contextualized bug reports.
Automated scripts began systematically filing private vulnerability reports across thousands of repositories simultaneously. Many of these submissions lacked reproducible proofs of concept, misunderstood the application context, or highlighted non-exploitable edge cases. Because these reports arrived via GitHub’s Private Vulnerability Reporting (PVR) channels, maintainers were legally and ethically obligated to review them before public disclosures or patches could safely move forward, effectively weaponizing compliance against the maintainers themselves.
GitHub’s Intervention (October 1, 2026)
Recognizing that maintainers were being buried to the point of operational paralysis, GitHub rolled out a two-pronged defense mechanism designed to optimize the intake stage:
- Daily Rate Limits: GitHub instituted strict, undisclosed daily thresholds on new private vulnerability reports. These limits apply both to individual accounts targeting specific repositories and across the platform more broadly. When a submitting account breaches the threshold, it is blocked from filing further reports that day and instructed to try again later.
- Structured Submission Forms: Abandoning the traditional single free-text description box, GitHub introduced structured reporting forms. Maintainers can now dictate the exact fields required for a report—such as mandatory reproducible proofs of concept, system environments, and affected version ranges—before a submission can be successfully processed.
Granular Repository Controls
To prevent these blanket restrictions from penalizing legitimate projects, GitHub empowered repository administrators with custom configuration tools. Project maintainers can now adjust overall daily reporting limits to suit their specific project sizes and team capacities. Furthermore, administrators can curate "allow lists" to exempt trusted security researchers, internal auditing staff, and established bug-bounty participants from the rate-limiting infrastructure.
These controls are integrated directly into the administrative settings of public repositories with Private Vulnerability Reporting enabled across GitHub Free, Pro, Team, and Enterprise Cloud tiers. Administrators can access and modify these parameters via the platform’s advanced security dashboard:
$$textSettings longrightarrow textAdvanced Security longrightarrow textPrivate Vulnerability Reporting$$
Crucially, GitHub’s rate limits apply exclusively to the creation of new reports. Once a vulnerability report has been successfully filed and is under active investigation, the communication channels—including comments attached to existing private advisories—remain entirely unrestricted. This ensures that ongoing collaborative triage between maintainers and valid reporters is not artificially throttled.
Supporting Context & Metrics: The Asymmetry of AI Security
To understand why rate limits were necessary, one must examine the fundamental economic and operational asymmetry currently plaguing software development. Finding a vulnerability has always been easier and cheaper than fixing it; AI has exponentially widened this gap.
[ AI-Generated Vulnerability Reports ]
               │
               ▼ (Massive Volume / Low Signal)
[ GitHub PVR Intake Gateway ] ──(Rate Limits & Structured Forms)──┐
                                                                ▼
[ Open-Source Maintainer Triage ] <─────────────────────────────┘
               │
               ▼ (Severe Bottleneck)
[ Patching & Remediation Process ]
During a recent industry webinar, Dan Lorenc, co-founder and CEO of software security firm Chainguard, articulated this imbalance with striking clarity. Lorenc noted that AI is "now finding vulnerabilities in the software they write and the software they use at a pace that is far exceeding defenders’ ability to patch and get updates and fix the vulnerabilities."
Lorenc famously summarized the modern security dilemma by observing that while finding bugs was historically straightforward, AI has essentially "poured another giant jug of gasoline onto the fire before inventing a better fire extinguisher."
While the developer ecosystem waits for fully automated remediation tools to catch up, the human factor remains the ultimate bottleneck. GitHub’s decision to cap inbound reporting volume is an acknowledgment that without artificial friction at the intake valve, human maintainers will simply abandon critical open-source projects due to burnout.
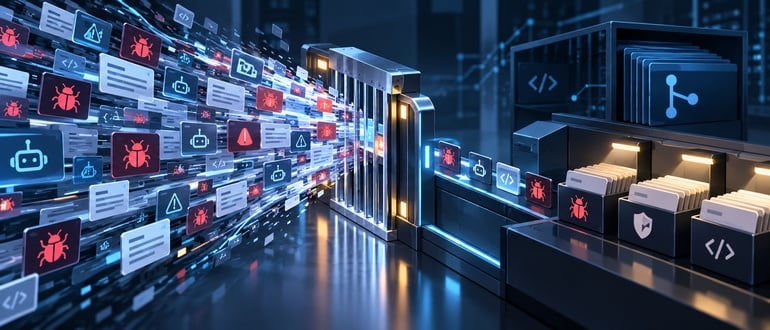
However, the lack of transparency regarding GitHub’s exact numerical thresholds has drawn mixed reactions from the security community. Because GitHub has chosen not to publish the specific numeric caps, researchers cannot calculate safe operating limits in advance. An automated script or poorly calibrated scanning bot will simply crash into the undisclosed ceiling, while legitimate security researchers running comprehensive multi-repo audits may find themselves unexpectedly locked out, sparking frustration among professional auditors.
Official Statements and Industry Perspectives
The introduction of rate limits has sparked robust debate across the software security landscape, shedding light on the broader implications of automated tooling in open-source maintenance.
GitHub positioned the updates as a necessary protective measure to preserve the integrity of the ecosystem. In its official change log documentation, the company emphasized that open-source maintainers were being inundated with bulk and automated filings that "bury the reports that matter." By filtering out the noise before it reaches the maintainer’s dashboard, GitHub aims to restore focus to actionable, high-severity vulnerabilities.
Industry leaders, meanwhile, view the move as a vital stopgap measure while the industry grapples with the wider fallout of generative AI.
Madelyn Olson, co-founder of the Valkyrie-derived database project Valkey, offered a pragmatic perspective during discussions at ValkeyConf in Prague. Highlighting how projects are adapting to the automated flood, Olson explained:
"We’ve created automated adversarial testing that looks for bugs and automated code reviews that generate pull requests (PR). Now, when you open a PR, we fine-tune a bot that looks for specific issues that are common in Valkey and is quite helpful at finding actual bugs."
Olson’s insights underscore a rising consensus: while AI caused the current triage crisis by scaling up bug creation, the long-term solution lies in deploying sophisticated, project-specific AI to handle the triage and remediation workflows as well.
Future Outlook: The Road Ahead for Open-Source Security
GitHub’s implementation of rate limits and structured reporting forms represents a critical evolutionary step in platform governance, but it is unlikely to be the final word on automated vulnerability management.
The Maintainer’s Dilemma: Tuning the Dials
In the immediate future, open-source maintainers will face a delicate balancing act. Project administrators must determine how aggressively to configure their repository-specific caps:
- Setting thresholds too low will successfully suppress noise but may create frustrating friction for legitimate, multi-faceted security audits conducted by trusted researchers.
- Setting thresholds too high will leave projects vulnerable to the exact triage fatigue and notification floods that necessitated GitHub’s intervention in the first place.
Toward Automated Triage and Remediation
Long-term sustainability in open-source security will require moving beyond simple quantitative rate-limiting toward intelligent qualitative filtering. As machine learning models become more deeply integrated into the development lifecycle, we can expect to see platforms evolve standardized protocols for machine-to-machine validation.
In this envisioned future, automated bug-reporting bots will be required to interface with automated verification sandboxes hosted by platforms like GitHub. These sandboxes will execute the proposed proof-of-concept exploit in an isolated environment, verify its validity, and assign a preliminary confidence score before human maintainers are ever notified.
Until that automated verification layer becomes a universal standard, GitHub’s rate limits and structured forms serve as a crucial defensive bulkhead. They establish a vital boundary between the relentless, algorithmic speed of artificial intelligence and the finite, invaluable cognitive capacity of the human beings who maintain the digital world.
Frequently Asked Questions
Why is GitHub limiting private vulnerability reports?
GitHub introduced these limits because open-source maintainers were being overwhelmed by an unsustainable surge of low-quality, bulk, and automated security reports generated by AI tools. This flood of noise often buried legitimate, high-severity security findings.
How many vulnerability reports can a user submit per day?
GitHub has chosen not to publicly disclose the exact numerical thresholds for its rate limits. Users who exceed the daily limit—whether targeting a specific repository or across the broader platform—are simply notified that they have hit the cap and must wait before submitting additional reports.
Can repository maintainers customize these reporting limits?
Yes. Repository administrators have full control to configure custom overall daily reporting limits tailored to their project’s capacity. Additionally, they can establish allow lists to exempt trusted security researchers, internal engineers, or verified bug-bounty participants from the rate-limiting rules.
Do these rate limits affect ongoing conversations about existing bug reports?
No. The rate limits apply strictly to the creation of new private vulnerability reports. Comments, code attachments, and collaborative investigations on reports that have already been successfully filed remain completely unrestricted.