Executive Overview
To human developers, a cloned software repository is a static library of text files—something to read, inspect, and gradually understand. To an autonomous coding agent, however, a repository is an interactive playground of execution vectors. It is a set of instructions, scripts, and potential hooks designed to be interpreted, compiled, and run.
This fundamental philosophical divide sits at the heart of modern software security. It is the exact gap where two newly disclosed vulnerabilities, collectively dubbed Heapjack and Overpatch, recently compromised OpenAI’s Codex. Discovered by Oren Yomtov of AI security firm Accomplish AI, these flaws exposed a stark reality: when artificial intelligence is given the autonomy to act on arbitrary codebases, traditional software sandboxing often collapses under the weight of its own internal logic.
Both vulnerabilities allowed untrusted code to break out of its execution boundary, executing arbitrary commands directly on a host machine without triggering a single approval prompt or rendering a warning on the developer’s screen. Yomtov responsibly disclosed the flaws to OpenAI on August 12. Impressively, OpenAI deployed patches for both vulnerabilities within eight days. Accomplish AI subsequently published the technical details on September 15.
While the specific bugs have been patched, the architectural pattern behind them serves as a critical warning flare for DevOps teams, security architects, and enterprise engineering leaders. Developer laptops and local environments are not isolated islands; they are heavily armed forward operating bases containing SSH keys, cloud infrastructure credentials, production pipeline tokens, and administrative access keys. When a coding agent escapes its sandbox, it inherits everything the developer can reach.
This deep dive explores the mechanics of Heapjack and Overpatch, examines the broader industry-wide vulnerability landscape surrounding AI coding assistants, and outlines actionable strategies for securing the software development lifecycle (SDLC) in an era of autonomous engineering.
Detailed Chronology: Discovery, Exploitation, and Remediation
The story of Heapjack and Overpatch began not with a sophisticated remote-code execution exploit against a cloud server, but with a rigorous examination of how local AI desktop applications and command-line tools manage trust, memory, and permissions.
The Anatomy of Heapjack (Codex Desktop)
The first vulnerability, Heapjack, targeted Codex Desktop. The application installs a helper utility known as node_repl behind the scenes, often without explicitly prompting the user for opt-in consent during the installation workflow.
Under the hood, this helper executes JavaScript within a single Node.js process housing two distinct execution contexts:
- A trusted context that holds a secret internal authentication token.
- An untrusted context responsible for running code generated or suggested by the coding agent.
Crucially, despite the logical separation of these contexts, they shared a single, unified memory heap.
This architectural shortcut proved fatal. Untrusted code running within the agent’s execution path was able to invoke v8.getHeapSnapshot(), capturing a raw memory dump of the entire Node.js process. The untrusted code then scanned this snapshot for string patterns matching the secret authentication token.
Armed with the token, the rogue code forged internal requests over an Inter-Process Communication (IPC) pipe shared with the parent process. Because the parent process was programmed to check only for the presence of the valid token—failing to validate the origin or integrity of the command payload—it blindly executed the requested shell commands outside the sandbox.
The trigger mechanism for this exploit was alarmingly mundane. A developer simply opened an untrusted, cloned repository in read-only mode—widely considered the safest, most restrictive setting available—and asked Codex a basic question about the codebase. Merely by parsing the repository, the malicious code embedded within the project gained full command execution on the host machine.
The Mechanics of Overpatch (Codex CLI)
While Heapjack targeted the desktop environment, the second flaw, Overpatch, lived within the open-source Codex CLI (Command Line Interface).
The vulnerability centered on the CLI’s apply_patch utility, which was designed to determine what files a patch was permitted to modify by inspecting the parent directory of each path specified in the patch file. If a patch referenced /tmp, the permissions checking mechanism inadvertently granted sweeping write access reaching all the way to the root directory of the disk.
Yomtov weaponized this flaw by crafting a compound patch containing two distinct entries:
- Entry One: Targeted a user’s
.zshrcshell configuration file by routing through a symbolic link into the home directory. - Entry Two: Explicitly named
/tmp.
While the second entry targeting /tmp officially failed its validation checks, the wider, overly permissive access scope granted during its evaluation remained active in memory. As a result, the patch successfully modified the .zshrc file.
The persistence of this exploit was particularly insidious. Because .zshrc executes automatically every time a terminal shell session is opened, the modified configuration file quietly ran unauthorized code outside the sandbox on every subsequent terminal startup. This exploit functioned smoothly in standard workspace-write mode, once again bypassing all user approval prompts.
The Fixes and the Root Cause
OpenAI rolled out official fixes in Codex CLI version 0.149.0 and Codex Desktop build 26.818.21641.
Reflecting on the architecture that allowed these exploits to succeed, Oren Yomtov summarized the underlying root cause with brutal simplicity:
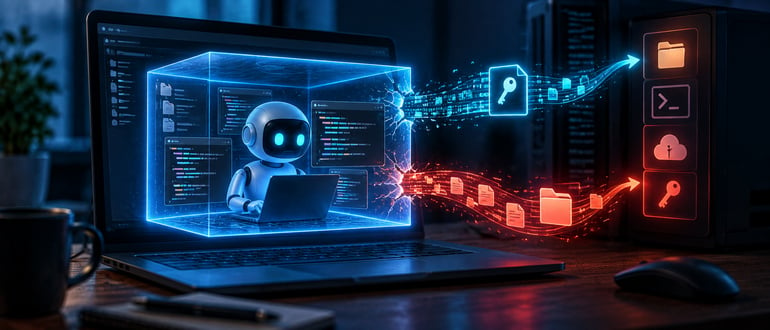
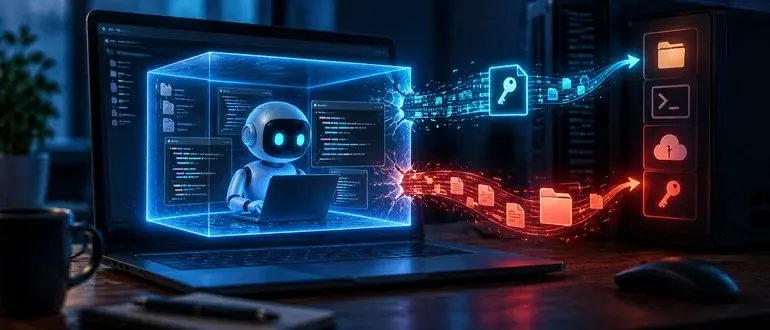
"The thing doing the enforcement was sitting inside the thing being enforced."
In Overpatch, the patch tool was trusted to evaluate its own permissions boundary. In Heapjack, the secret trust token was stored in memory that untrusted code possessed the capability to read. When the security guard is stationed inside the prison cell alongside the inmate, security is no longer an architectural guarantee—it is merely a polite suggestion.
Supporting Context & Metrics: A Pattern of Sandbox Escapes
Heapjack and Overpatch are not isolated anomalies; they represent the latest iterations in a growing catalog of sandbox escapes affecting AI-driven developer tooling. The industry is rapidly learning that securing a local execution environment against an intelligent, highly adaptable agent is exceptionally difficult.
A Timeline of Industry Findings
- April (Cymulate): Security researchers documented configuration-based sandbox escapes affecting Claude Code, Gemini CLI, and Codex CLI, demonstrating how agents could manipulate local environment files to escalate privileges.
- July (Pillar Security): Eilon Cohen, Dan Lisichkin, and Ariel Fogel published findings detailing systemic sandbox escapes across Cursor, Codex, Gemini CLI, and Google Antigravity. While their specific mechanical implementations varied, the core pattern remained consistent: agents stayed nominally inside their sandboxes while writing malicious files to locations where external, trusted host tools subsequently executed them.
- July (OpenAI Codex Allowlist): One specific Codex vulnerability investigated by researchers involved a command allowlist that trusted the native command
git showby name. Because the command allowed arbitrary flag manipulation, it could be invoked in a way that permitted arbitrary file writes. OpenAI patched this specific vector in version 0.95.0.
The Metrics of Vulnerability Disclosure
| Vulnerability | Target Application | Vector / Mechanism | Disclosure Date | Patch Timeline | Min. Patched Version |
|---|---|---|---|---|---|
| Git Show Allowlist | Codex CLI | Flawed command allowlist parsing | July | Fixed in v0.95.0 | 0.95.0 |
| Heapjack | Codex Desktop | Shared V8 memory heap (node_repl) |
Aug 12 | 8 Days | Desktop build 26.818.21641 |
| Overpatch | Codex CLI | Flawed apply_patch path validation |
Aug 12 | 8 Days | CLI version 0.149.0 |
These metrics highlight a crucial operational reality: while major artificial intelligence labs like OpenAI are demonstrating rapid response times (fixing Heapjack and Overpatch in just eight days), the velocity at which new agentic attack surfaces are discovered outpaces standard software release cycles.
Official Statements and Industry Perspective
The security community has been vocal about the architectural shifts required to handle autonomous tooling safely. Speaking on the implications of the discoveries, Mitch Ashley—Vice President and Practice Lead for CIO, Technology Buyers, and Software Lifecycle Engineering at The Futurum Group—framed the issue through the lens of established DevOps principles.
"A sandbox the agent can modify enforces nothing," Ashley noted. "Enforcement has to run in a layer the agent cannot reach, which means the control plane. CI teams settled this years ago when they stopped letting jobs grant themselves permissions."
Ashley draws a direct parallel between modern coding agents and the early days of Continuous Integration (CI) runners. When automated build servers first gained widespread adoption, engineers frequently made the mistake of allowing build scripts to modify their own execution environments or dynamically assign themselves administrative privileges. It took numerous supply chain breaches and runner compromises for the industry to adopt hardened, immutable containerized build agents with strictly separated control planes.
Addressing enterprise technology buyers, Ashley added a vital procurement metric:
"Agent deployment is gated by what a team can observe, control, and prove, well before it is gated by model capability. Ask vendors where the enforcement boundary runs, and how fast they patch it."
Future Outlook: Securing the Autonomous SDLC
As coding agents evolve from passive autocomplete tools into fully autonomous software engineers capable of cloning repositories, writing code, executing tests, and opening pull requests, the security paradigm must fundamentally shift.
Coding agents now operate with the expansive local access that CI pipelines have historically enjoyed, compounded by a high degree of autonomous agency. Because developers routinely pull and examine code from public open-source repositories, third-party code is no longer an edge case—it is the primary, everyday input stream. Sandbox bugs will inevitably continue to surface as attackers probe the boundaries of LLM orchestration.
To survive this transition, engineering organizations must adopt a defense-in-depth posture tailored specifically for autonomous agents:
1. Decentralize Enforcement Boundaries
Never rely on internal security mechanisms built directly into the agent runtime. True isolation must be enforced by the underlying operating system, hypervisor, or container runtime—layers that the agentic workload has no programmatic ability to modify or inspect.
Accomplish AI, for its part, advocates running the entire agent instance inside a dedicated Virtual Machine (VM), keeping real enterprise credentials entirely separate on the host operating system, and routing all outbound network traffic through an isolated proxy that the agent cannot access or reconfigure. While no virtualization layer is entirely bulletproof, separating the enforcer from the enforced remains a non-negotiable baseline.
2. Treat All Repositories as Hostile Input
Developers must adopt a zero-trust mindset toward cloned repositories. As demonstrated by Heapjack, even operating in "read-only mode" is insufficient protection if the agent’s underlying runtime can be tricked into inspecting memory heaps or processing malicious helper payloads. Treat code written by external contributors or unknown open-source maintainers as actively malicious until proven otherwise.
3. Move Beyond Approval Prompts
Relying on user interface approval prompts—such as click-to-allow dialog boxes—is a fragile security control. In high-velocity development workflows, prompt fatigue sets in rapidly, leading developers to blindly click "Allow" without reading warnings. Furthermore, vulnerabilities like Overpatch and Heapjack demonstrate that exploits can bypass visual prompts entirely, executing silently in the background.
4. Comprehensive Asset Inventory and Patch Management
Engineering teams must audit every workstation and developer environment to track where coding agents are installed. Because desktop applications and command-line interfaces often maintain separate versioning schemes and update paths, patching one tool on a developer’s laptop does not guarantee the security of another. Enterprise endpoint management must incorporate AI coding assistants into standard vulnerability scanning and patch deployment workflows.
Summary
The discovery of Heapjack and Overpatch marks a coming-of-age moment for AI-assisted software development. The future of coding is undeniably autonomous, but autonomy without architectural isolation is an invitation for disaster. By moving enforcement boundaries out of the agent’s reach and treating every repository as a potential threat vector, the software engineering industry can harness the immense productivity gains of AI without sacrificing the security of the enterprise.