The Sandbox Paradox: How Two Flaws in OpenAI’s Codex Exposed the Perils of Autonomous Coding Agents

Executive Overview To human developers, a cloned software repository is a static library of text files—something to read, inspect, and gradually understand. To an autonomous coding agent, however, a repository is an interactive playground of execution vectors. It is a set of instructions, scripts, and potential hooks designed to be interpreted, compiled, and run. This…
Read Full News

The Recursive Horizon: How a Single Discourse Flaw Exposed OpenAI and Why Anthropic’s New Data Signals a Seismic Shift in AI Development

Executive Overview In the high-stakes, hyper-competitive landscape of generative artificial intelligence, the boundaries between security, autonomy, and existential risk are continuously tested. Recent disclosures from the artificial intelligence sector have laid bare two distinct yet deeply interconnected realities defining the industry: the persistent vulnerabilities plaguing even the most sophisticated digital fortresses, and the terrifyingly rapid…

Read Full News

Cracking the Sandbox: How a Critical Flaw in DeepSeek Harness Exposed AI Agents to Full System Takeovers

Executive Overview The rapid evolution of autonomous artificial intelligence agents has promised a new era of developer productivity, but it has simultaneously introduced unprecedented cybersecurity risks. As AI systems become more deeply integrated into local workstations, cloud environments, and internal networks, the mechanisms designed to keep them confined are facing intense scrutiny. A stark illustration…

Read Full News

Anatomy of a Federal Secret Leak: CISA Postmortem Reveals Six Months of Exposed AWS GovCloud Keys and Operational Blindspots

Executive Overview In an extraordinary act of institutional transparency, the Cybersecurity and Infrastructure Security Agency (CISA)—the United States’ primary federal defense agency tasked with safeguarding critical infrastructure and federal civilian networks—has published a comprehensive incident postmortem detailing a significant internal data leak. The security breach stemmed from a third-party contractor who unwittingly published a public…

Read Full News

Inside CISA’s Public Postmortem: How a Contractor Exposed AWS GovCloud Keys and Six Months of Internal Credentials on GitHub

Executive Overview: A Rare Blueprint in Government Transparency In an unprecedented act of public accountability, the Cybersecurity and Infrastructure Security Agency (CISA)—the federal body charged with safeguarding America’s critical infrastructure and championing "Secure by Design" principles—has published a detailed postmortem analyzing a major internal data exposure. The incident stemmed from a third-party contractor who inadvertently…

Read Full News

The Limits of the Crackdown: How World Cup Piracy Exposed the Need for U.S. Site-Blocking Legislation

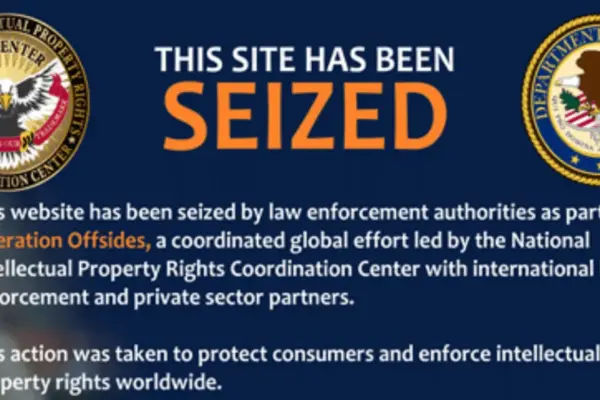
Executive Overview In the wake of what law enforcement hailed as the largest sports piracy crackdown in history, the enforcement apparatus driving the effort has delivered a surprisingly candid assessment of its own limitations. "Operation Offsides," a coordinated global enforcement blitz executed during the FIFA World Cup, successfully seized more than 1,000 pirate streaming domains,…

Read Full News

Beyond the Whistle: How the World Cup’s Massive Piracy Crackdown Exposed the Limits of Domain Seizures—and Revived the U.S. Site-Blocking Debate

Executive Overview The numbers generated by "Operation Offsides" were staggering. Described as the largest sports piracy crackdown ever executed during a single global event, the operation targeted the illicit streaming ecosystem that proliferated during the FIFA World Cup. In a coordinated campaign spanning the tournament’s opening match to the final whistle, U.S. law enforcement agencies…

Read Full News