AI-Driven Vulnerability Discovery Triggers Record-Breaking Patch Tuesday: Microsoft Fixes Over 570 Flaws Amid Industry-Wide Shifts

Executive Overview In an unprecedented intelligence-driven update cycle, Microsoft Corp. released security updates addressing at least 570 security vulnerabilities across its Windows operating systems and peripheral software ecosystem. The massive update almost triples the record-breaking figures established in the software giant’s previous Patch Tuesday cycle, marking a dramatic inflection point in vulnerability management. Microsoft explicitly…

Read Full News

Silent Bandwidth Harvesting: LG Orders Removal of Residential Proxy SDKs from Smart TV Ecosystem

Executive Overview In a decisive move to reclaim control over its smart TV ecosystem and protect consumer privacy, consumer electronics titan LG Electronics USA has announced a sweeping ban on apps that covertly turn smart televisions into always-on residential proxy nodes. The corporate policy shift comes in the direct wake of alarming research revealing that…

Read Full News

The AI Bugpocalypse: Microsoft Issues 398 Fixes in Massive August Update as Automated Discovery Reshapes Vulnerability Management

Executive Overview In an unprecedented acceleration of software security maintenance, Microsoft released updates to remediate at least 398 security vulnerabilities across its Windows operating systems and associated enterprise software stack. The massive release marks one of the largest single-day security updates in computing history, second only to the company’s record-shattering release of over 570 updates…

Read Full News

Unmasking the Fengwo Empire: How Budget Android Streaming Devices Drive a Global AI Ad-Fraud Syndicate

Executive Overview For years, cybersecurity analysts and law enforcement agencies have warned consumers against the purchase of off-brand, generic streaming set-top boxes promising "unlimited content" for a one-time fee. Historically, these cheap devices were known to quietly monetize their users’ internet connections by turning home networks into residential proxy nodes for third parties. However, a…

Read Full News

Fall of the Spider: Key Members of Prolific Hacktivist Group Plead Guilty to Critical Infrastructure and Healthcare Cyberattacks

Executive Overview In a dramatic turning point for global cyber law enforcement, two core members of the notorious cybercrime syndicate known as Scattered Spider entered guilty pleas in a London courtroom this week. The surrenders occurred on the very first day of what was projected to be a protracted six-week criminal trial, signaling a definitive…

Read Full News

Unmasking the Invisible Tracker: How DecryptAds Exposes the Hidden Cyber Risks of Modern Adtech

Executive Overview For over two decades, the global digital advertising ecosystem has operated behind an opaque curtain. While millions of web users interact daily with mainstream news outlets, streaming services, and mobile applications, a labyrinthine infrastructure of data brokers, supply-side platforms (SSPs), and ad exchanges silently tracks user behavior, harvests sensitive telemetry, and executes real-time…

Read Full News

Inside the Snowflake Siege: The Fall of Connor Moucka and the $2.5 Million Cyber Extortion Syndicate

Executive Overview In one of the most significant legal developments in modern cloud-focused cybercrime, 26-year-old Canadian national Connor Riley Moucka has pleaded guilty in a United States federal court to multiple criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy. Operating under online monikers such as "Judische" and "Waifu," Moucka admitted to…

Read Full News

Federal Coordinated Action Seizes NetNut Infrastructure, Unraveling Popa Botnet and Israeli Parent Company Alarum Technologies

Executive Overview In one of the most significant law enforcement interventions against commercial proxy abuse to date, the Federal Bureau of Investigation (FBI) and the Internal Revenue Service Criminal Investigation (IRS-CI) division, in coordination with global technology leaders, have seized hundreds of internet domains powering NetNut, a massive residential proxy network operated by the publicly…

Read Full News

Executive Overview

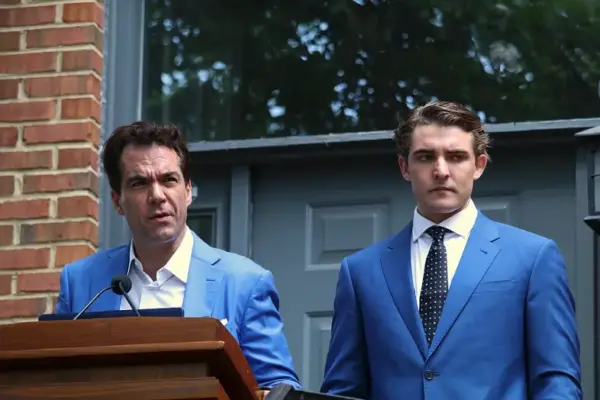
In a dramatic crossover between political disinformation, federal criminal law, and offensive cyber operations, a Virginia-based cybersecurity startup dangling multimillion-dollar payouts for zero-day software exploits has been identified as the latest venture of convicted felons and far-right conspiracy theorists Jacob Wohl and Jack Burkman. Operating under the brand name IRIS C2 and backed by a…

Read Full News

Postmortem Analysis: Inside CISA’s Six-Month GitHub Secret Leak and Incident Response Failures

Executive Overview In an unprecedented move toward operational transparency, the Cybersecurity and Infrastructure Security Agency (CISA) has released a comprehensive postmortem detailing a severe, multi-month data leak caused by a third-party contractor. For nearly six months, an unencrypted public GitHub repository titled "Private CISA" hosted 844 megabytes of sensitive agency infrastructure data. The exposed records…

Read Full News