Inside the Snowflake Extortion Syndicate: Mastermind Connor Moucka Pleads Guilty to Historic Cloud Hacking Campaign

Executive Overview In one of the most destructive and high-profile cybercrime prosecutions in recent history, 26-year-old Canadian national Connor Riley Moucka has formally pleaded guilty in U.S. federal court to computer fraud, wire fraud, aggravated identity theft, and conspiracy. Described by federal prosecutors and cybersecurity researchers as one of the most prolific threat actors of…
Read Full News

Shadow Brokerage or Serial Scam? Convicted Felons Jacob Wohl and Jack Burkman Reemerge with Zero-Day Cybersecurity Venture

Executive Overview A newly surfaced cybersecurity startup offering multi-million-dollar bounties for high-tier zero-day software vulnerabilities has been unmasked as the latest venture of convicted felons and far-right political provocateurs Jacob Wohl and Jack Burkman. Operating under the moniker IRIS C2 (promoted via the X account @C2IRIS) and registered through a Virginia entity known as Calvexa…

Read Full News

Inside CISA’s Public Postmortem: How a Contractor Exposed AWS GovCloud Keys and Six Months of Internal Credentials on GitHub

Executive Overview: A Rare Blueprint in Government Transparency In an unprecedented act of public accountability, the Cybersecurity and Infrastructure Security Agency (CISA)—the federal body charged with safeguarding America’s critical infrastructure and championing "Secure by Design" principles—has published a detailed postmortem analyzing a major internal data exposure. The incident stemmed from a third-party contractor who inadvertently…

Read Full News

The AI-Accelerated Vulnerability Crisis: Microsoft Patches Record 570 Security Flaws in Epoch-Defining Release

Executive Overview In an unprecedented shift that underscores the dramatic impact of artificial intelligence on cybersecurity operations, Microsoft Corp. released software updates addressing at least 570 security vulnerabilities across its Windows operating systems and software suite. The record-smashing Patch Tuesday release—nearly tripling the volume of the company’s previous historic update set just one month prior—signals…

Read Full News

Inside the Takedown of TeamPCP: How Law Enforcement Unmasked the Masterminds Behind the Largest Software Supply Chain Attack Spree

Executive Overview In a milestone international law enforcement operation, the Australian Federal Police (AFP), working in close coordination with the Federal Bureau of Investigation (FBI) and the Western Australia Police Force (WAPF), has dismantled the primary operational core of TeamPCP. The prolific cybercrime and data extortion syndicate is widely credited with engineering the longest-running, most…

Read Full News

LG Moves to Purge Residential Proxy SDKs from Smart TV App Store Following Security Findings

Executive Overview In a major policy shift targeting covert internet traffic routing across consumer hardware, home appliance giant LG Electronics USA has announced a strict ban on smart TV applications that transform televisions into always-on residential proxy nodes. The decision follows alarming research revealing that more than four out of ten applications on LG’s native…

Read Full News

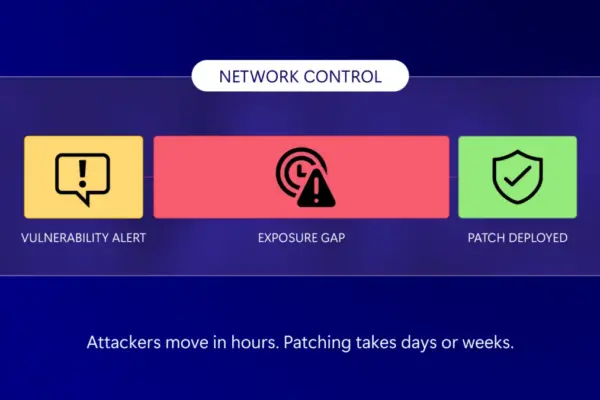
The Collapse of the Patch Window: How AI and Cloud Complexity Are Forcing a Paradigm Shift in Enterprise Cybersecurity

Executive Overview For decades, the foundation of enterprise cybersecurity rested upon a predictable lifecycle: a software vulnerability would be publicly disclosed, enterprise security teams would evaluate their organizational exposure, patches would be regression-tested in staging environments, and system administrators would schedule maintenance windows to deploy fixes into production. This traditional cadence operated under the fundamental…

Read Full News

Microsoft Unveils Massive 398-Vulnerability Patch Bundle as AI Accelerates Security Discoveries

Executive Overview In an extraordinary continuation of recent enterprise patch volume trends, Microsoft released security updates addressing no fewer than 398 vulnerabilities across its Windows operating systems and supported software ecosystem. The release features a zero-day flaw actively exploited in the wild, two previously disclosed vulnerabilities, and 42 security bugs categorized with Redmond’s highest severity…

Read Full News

The Botnet in Your Living Room: Inside the Multi-Million Dollar Ad Fraud and Proxy Syndicate Powered by Generic Android TV Boxes

Executive Overview For years, cybersecurity analysts and law enforcement agencies have warned consumers about the hidden dangers of unbranded Android TV streaming devices. Frequently advertised on major e-commerce platforms with promises of "unlimited free content" for a low, one-time fee, these budget electronics have long been suspected of secretly harvesting bandwidth and operating as nodes…

Read Full News

Key Scattered Spider Hackers Plead Guilty in UK Over Transport for London Cyberattack and Global Extortion Spree

Executive Overview In a dramatic turn of events on the opening day of a scheduled six-week trial in London, two central operatives of the infamous cybercrime syndicate known as Scattered Spider entered guilty pleas to criminal charges arising from a devastating August 2024 cyberattack against Transport for London (TfL). The cyber incident severely disrupted public…

Read Full News