Unmasking TeamPCP: Inside the Fall of the World’s Most Destructive Software Supply Chain Syndicate

Executive Overview In what law enforcement agencies are calling one of the most critical cybercrime disruptions of the decade, the Australian Federal Police (AFP), working in tandem with the Federal Bureau of Investigation (FBI) and Western Australia Police Force (WAPF), has dismantled the core operational ring of TeamPCP. Responsible for the longest-running and most destructive…
Read Full News

The AI-Driven Bugpocalypse: Microsoft Remediates 398 Security Flaws in Record-Setting August Patch Release

Executive Overview In an era where artificial intelligence is fundamentally rewriting the economics of vulnerability discovery, corporate IT departments and cybersecurity defenders are confronting an unprecedented operational challenge. Microsoft today issued software updates to resolve an extraordinary 398 security vulnerabilities across its Windows operating systems and ecosystem software. Coming on the heels of July’s historic…

Read Full News

Massive Dark Web Leak Exposes 153 Million Driver’s Licenses: Inside the Nexus Market Breach and the IDScan.net Crisis

Executive Overview In one of the most severe supply-chain data breaches in history, a cybercrime entity operating under the moniker Nexus launched a dark web marketplace selling high-resolution digital scans of identity documents belonging to more than 170 million individuals across North America. Among the stolen assets are over 153 million state and provincial driver’s…

Read Full News

Landmark Court Order Strips Data Broker Radaris of Web Domains Following Privacy Law Violations

Executive Overview In a unprecedented setback for the commercial data broker industry, the prominent people-search platform Radaris.com has been forced to surrender its primary domain name—along with more than a dozen affiliated websites—following a high-stakes legal battle in New Jersey. Long notorious among privacy advocates for ignoring opt-out requests and maintaining an elusive corporate structure,…

Read Full News

AI-Accelerated Vulnerability Discovery Triggers Unprecedented 974-Bug Patch Release, Straining Enterprise Defenses

Executive Overview In an unprecedented milestone for software security, Microsoft Corp. has released a massive monthly security update package containing fixes for at least 974 security vulnerabilities across its Windows operating systems and ecosystem software. The colossal patch bundle represents the largest single security release in the software giant’s history, shattering its previous record set…

Read Full News

Unveiling the Shadow Economy: How DecryptAds Exposes Global Adtech Supply Chain Risks, Malvertising, and AI Slop Operations

Executive Overview For over two decades, the global programmatic advertising ecosystem has functioned as a hyper-complex, opaque marketplace. Every millisecond, billions of automated auctions dictate which advertisements appear on mobile screens, desktop browsers, and smart televisions across the globe. Concurrently, an sprawling network of data brokers, supply-side platforms (SSPs), demand-side platforms (DSPs), and obscure intermediaries…

Read Full News

Unmasking the Snowflake Hackers: Inside the High-Stakes Cloud Extortion Campaign That Rattled Corporate America

1. Executive Overview In one of the most significant legal developments in recent cybercrime history, 26-year-old Canadian national Connor Riley Moucka has formally pleaded guilty in federal court to computer fraud, wire fraud, aggravated identity theft, and conspiracy. Operating under online aliases such as "Judische" and "Waifu," Moucka was identified by federal authorities as a…

Read Full News

Inside CISA’s Six-Month Credential Exposure: Lessons from the Cyber Agency’s Landmark Postmortem

Executive Overview In an unprecedented display of public accountability, the Cybersecurity and Infrastructure Security Agency (CISA)—the United States’ lead federal authority on cybersecurity and critical infrastructure protection—has released a comprehensive postmortem detailing a significant internal security lapse. For nearly six months, an unencrypted public GitHub repository maintained by a third-party contractor exposed administrative credentials, internal…

Read Full News

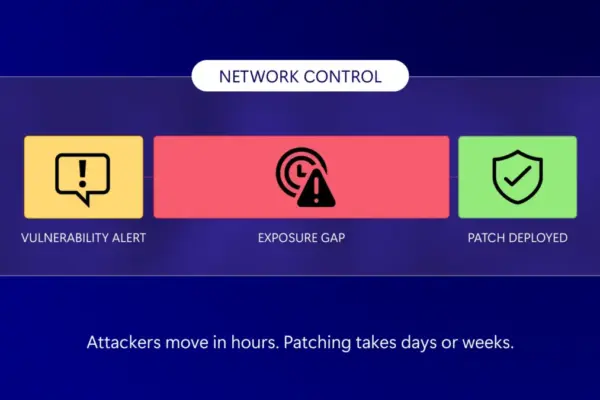
The Death of the Patch Window: How AI and Cloud Complexity Are Forcing a Paradigm Shift in Cybersecurity

Executive Overview For nearly three decades, corporate cybersecurity operated on a predictable, linear model: a software vulnerability was publicly disclosed, security operations teams assessed their exposure, engineers tested vendor-supplied fixes in staging environments, and patches were deployed during scheduled maintenance windows. This traditional workflow relied on a single fundamental premise—that enterprise defenders could move faster…

Read Full News

AI-Powered Discovery Triggers Record 570-Vulnerability Patch Tuesday Release by Microsoft

Executive Overview In an unprecedented shift that underscores the transformative impact of artificial intelligence on cybersecurity, Microsoft Corp. has released software updates to address a staggering 570 security vulnerabilities across its Windows operating systems and broader software portfolio. This massive release nearly triples the previous record set by the company, signaling a fundamental evolution in…

Read Full News