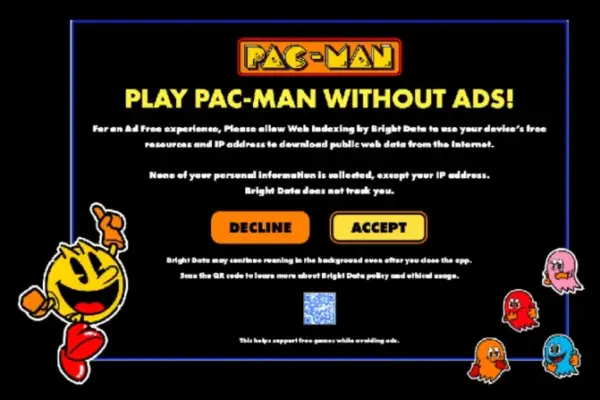
LG Moves to Purge Residential Proxy SDKs from Smart TV App Store Following Security Findings

Executive Overview In a major policy shift targeting covert internet traffic routing across consumer hardware, home appliance giant LG Electronics USA has announced a strict ban on smart TV applications that transform televisions into always-on residential proxy nodes. The decision follows alarming research revealing that more than four out of ten applications on LG’s native…
Read Full News

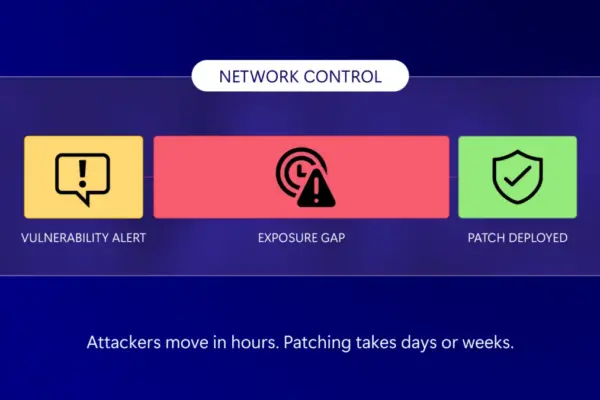
The Collapse of the Patch Window: How AI and Cloud Complexity Are Forcing a Paradigm Shift in Enterprise Cybersecurity

Executive Overview For decades, the foundation of enterprise cybersecurity rested upon a predictable lifecycle: a software vulnerability would be publicly disclosed, enterprise security teams would evaluate their organizational exposure, patches would be regression-tested in staging environments, and system administrators would schedule maintenance windows to deploy fixes into production. This traditional cadence operated under the fundamental…

Read Full News

Microsoft Unveils Massive 398-Vulnerability Patch Bundle as AI Accelerates Security Discoveries

Executive Overview In an extraordinary continuation of recent enterprise patch volume trends, Microsoft released security updates addressing no fewer than 398 vulnerabilities across its Windows operating systems and supported software ecosystem. The release features a zero-day flaw actively exploited in the wild, two previously disclosed vulnerabilities, and 42 security bugs categorized with Redmond’s highest severity…

Read Full News

The Botnet in Your Living Room: Inside the Multi-Million Dollar Ad Fraud and Proxy Syndicate Powered by Generic Android TV Boxes

Executive Overview For years, cybersecurity analysts and law enforcement agencies have warned consumers about the hidden dangers of unbranded Android TV streaming devices. Frequently advertised on major e-commerce platforms with promises of "unlimited free content" for a low, one-time fee, these budget electronics have long been suspected of secretly harvesting bandwidth and operating as nodes…

Read Full News

Key Scattered Spider Hackers Plead Guilty in UK Over Transport for London Cyberattack and Global Extortion Spree

Executive Overview In a dramatic turn of events on the opening day of a scheduled six-week trial in London, two central operatives of the infamous cybercrime syndicate known as Scattered Spider entered guilty pleas to criminal charges arising from a devastating August 2024 cyberattack against Transport for London (TfL). The cyber incident severely disrupted public…

Read Full News

Unmasking the Shadow Ecosystem: How DecryptAds Exposes Malvertising, Foreign Surveillance, and Adtech Supply-Chain Risks

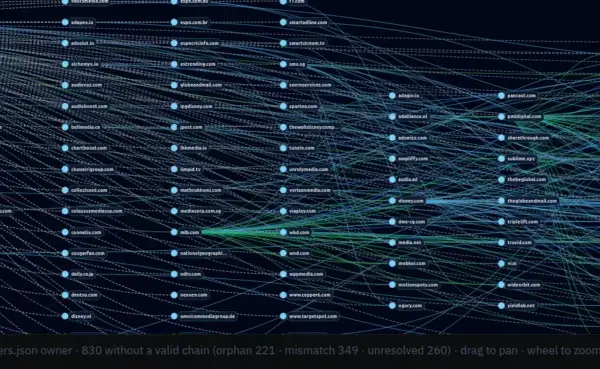
Executive Overview: Unveiling the Opaque Adtech Supply Chain For over two decades, the digital advertising ecosystem has operated behind a veil of intentional complexity. While millions of web pages and mobile applications harvest user telemetry, serve display ads, and process real-time bidding requests every second, the underlying network of data brokers, ad exchanges, and monetization…

Read Full News

Mastermind of Massive Cloud Extortion Campaign Pleads Guilty in U.S. Federal Court

Executive Overview In one of the most significant legal breakthroughs against modern cybercrime rings, Connor Riley Moucka—a 26-year-old Canadian national previously identified by cybersecurity researchers as one of the most destructive threat actors of 2024—has formally pleaded guilty in a U.S. federal court. Moucka admitted to his pivotal role in a widespread conspiracy to hack,…

Read Full News

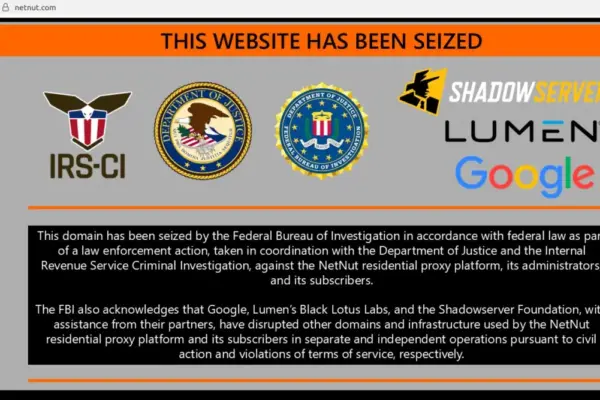
Federal Law Enforcement Dismantles NetNut Proxy Network and Massive Popa Botnet Linked to Nasdaq-Traded Firm

Executive Overview In one of the most significant law enforcement operations targeting commercial cybercrime infrastructure in recent years, the Federal Bureau of Investigation (FBI), in coordination with the Internal Revenue Service Criminal Investigation (IRS-CI) division and a coalition of global technology leaders, has seized hundreds of domains powering NetNut, a massive commercial residential proxy network….

Read Full News

The Anatomy of a Zero-Day Charade: How Two Notorious Conspiracists Rebranded as Offensive Cyber Brokers

Executive Overview A newly emerged cybersecurity venture promising multi-million-dollar bounties for zero-day software exploits has been identified as the latest front operation engineered by two of America’s most prolific political disinformation artists and convicted felons. Operating under the brand IRIS C2 and registered corporately as Calvexa Group LLC, the firm claims to procure high-tier cyber-weapons…

Read Full News

Anatomy of a Federal Security Exposure: CISA Releases Postmortem Following Months-Long Credential Leak on GitHub

Executive Overview In an extraordinary display of institutional transparency following an operational breach, the Cybersecurity and Infrastructure Security Agency (CISA)—the United States government’s premier civilian cyber defense organization—has published a detailed postmortem analyzing a major internal data leak. The security incident involved an embedded contractor who inadvertently exposed sensitive administrative credentials, AWS GovCloud access keys,…

Read Full News