Securing the Modern Software Supply Chain: Engineering Confidence Crumbles Under the Weight of AI and Machine-Speed Attacks

Executive Overview The modern software supply chain is facing an existential crisis of confidence. According to a comprehensive new survey commissioned by software artifact management platform provider Cloudsmith—polling 400 platform and security engineers across the United States and the United Kingdom—nearly three-quarters of technical professionals harbor profound doubts about the efficacy of their current security…
Read Full News

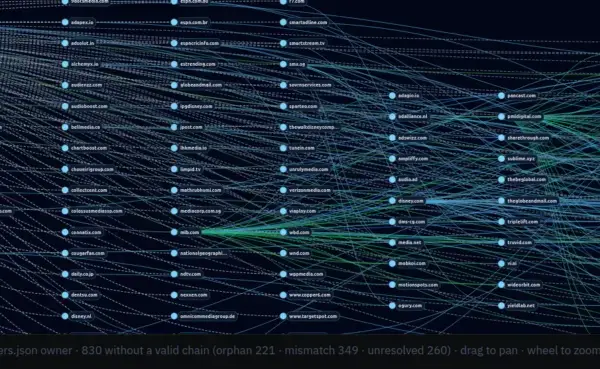
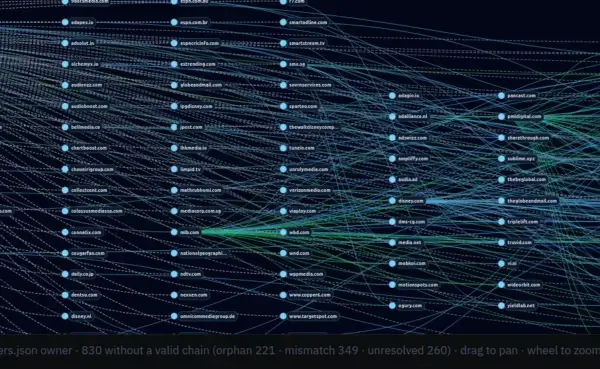
Unveiling the Hidden AdTech Supply Chain: How DecryptAds Exposes Global Surveillance, Malvertising, and Geopolitical Threats

Executive Overview The modern digital ecosystem relies heavily on programmatic advertising to monetize web traffic, mobile applications, and connected devices. However, behind the seamless presentation of online content lies a vast, highly opaque web of adtech intermediaries, data brokers, real-time bidding (RTB) exchanges, and tracking networks. For over a decade, determining which corporate entities are…

Read Full News

The Great Bypass: How "Shadow AI" is Fracturing the Digital Asset Supply Chain and Why Traditional Governance is Failing

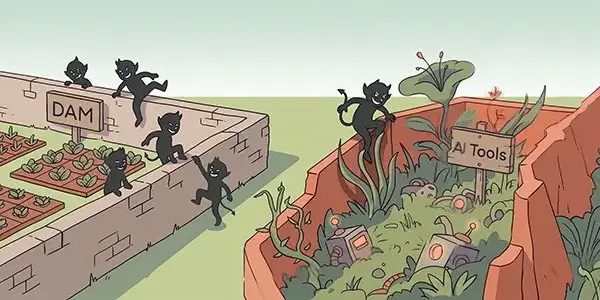
Executive Overview In the modern enterprise, a quiet yet profound operational rebellion is taking place on the desks of creative professionals. A recent landmark survey published by Santa Cruz Software and analyzed by digital asset management (DAM) expert Ralph Windsor reveals a staggering paradox at the heart of corporate technology strategy: 96 percent of organizations…

Read Full News

Dismantling TeamPCP: Inside the Fall of Cybercrime’s Most Prolific Supply Chain Syndicate

Executive Overview In a milestone operation against global cybercrime, the Australian Federal Police (AFP), working alongside the Federal Bureau of Investigation (FBI) and the Western Australia Police Force (WAPF), have arrested two Western Australian men linked to TeamPCP. The syndicate is widely regarded by cybersecurity analysts as the perpetrator behind the longest-running and most disruptive…

Read Full News

The Paradigm Shift in Software Supply Chain Security: Why Gate-Based Enforcement and Edge-Native Policies Are Becoming Table Stakes

Executive Overview The software supply chain security ecosystem has reached a profound architectural inflection point. For over a decade, organizations operated under a reactive posture: dependencies were pulled into build environments on demand, scanned after installation, and flagged for vulnerabilities via traditional Common Vulnerabilities and Exposures (CVE) databases. Today, that model is obsolete. Accelerated by…

Read Full News

Breaking the Chain: How Modal Motors is Redefining U.S. Hard Tech Without Chinese Rare-Earth Elements

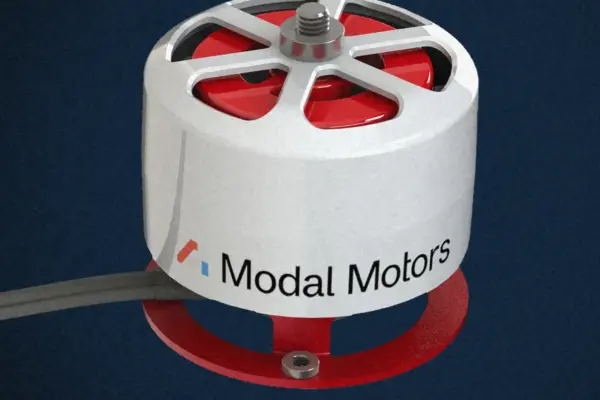
Executive Overview The global race to secure supply chains for critical hardware—ranging from military-grade autonomous drones to warehouse robotics—has reached a critical juncture. As policymakers in Washington and Brussels push aggressively to reshore manufacturing, a consensus has emerged that dependence on foreign entities, particularly China, represents a foundational vulnerability for Western national security and economic…

Read Full News

The Shadow AI Crisis: Why Creative Teams Are Ignoring Corporate Rules—And How to Fix the Digital Asset Supply Chain

By Investigative Tech Desk Published: September 2026 Executive Overview The modern enterprise is locked in a silent, high-stakes battle between rigid corporate compliance and the relentless velocity of creative production. According to a striking new industry survey published by digital asset management (DAM) tool provider Santa Cruz Software, a staggering 96% of organizations are currently…

Read Full News

Sophisticated Supply Chain Attack on npm Evolving Past Traditional Defenses with Smart Contract C2 and Runtime Malice

Executive Overview The JavaScript ecosystem has once again been rattled by a sophisticated, highly calculated software supply chain campaign targeting the npm (Node Package Manager) registry. Discovered and analyzed by security researchers at Checkmarx, the attack hinges on a malicious package named indexed-btree, which masquerades as a legitimate dependency (sorted-btree). Amassing nearly two million weekly…

Read Full News

Unveiling the Digital Surveillance Economy: How DecryptAds Exposes the Hidden Adtech Supply Chain, Malvertising, and Geopolitical Risks

Executive Overview For decades, the multi-billion-dollar digital advertising ecosystem has operated behind a veil of intentional complexity. While everyday internet users navigate commercial websites and mobile applications, a vast, invisible network of data brokers, supply-side platforms (SSPs), demand-side platforms (DSPs), and ad exchanges silently harvest behavioral telemetry, device fingerprints, and precise geolocation coordinates. Although industry-standard…

Read Full News

Unmasking TeamPCP: Inside the Fall of the World’s Most Destructive Software Supply Chain Syndicate

Executive Overview In what law enforcement agencies are calling one of the most critical cybercrime disruptions of the decade, the Australian Federal Police (AFP), working in tandem with the Federal Bureau of Investigation (FBI) and Western Australia Police Force (WAPF), has dismantled the core operational ring of TeamPCP. Responsible for the longest-running and most destructive…

Read Full News