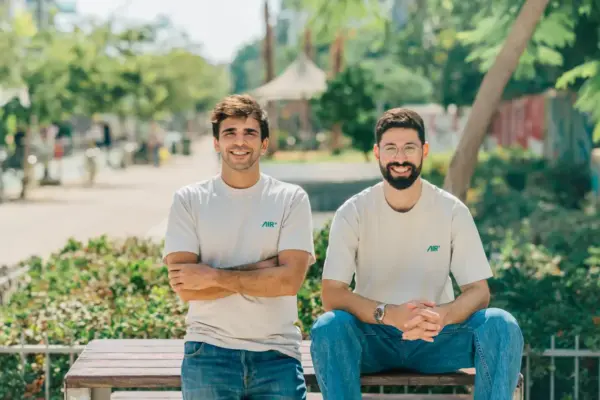
Securing the Autonomous Frontier: AI Security Startup AIR Emerges From Stealth With $50 Million to Guard the Emerging Agent Supply Chain

Executive Overview As artificial intelligence rapidly transitions from a conversational novelty to an autonomous operational force within the enterprise, a hidden security crisis is quietly taking shape. Modern corporations are no longer just deploying chatbots; they are giving AI agents deep, functional access to internal databases, mission-critical enterprise systems, and the open internet. To achieve…
Read Full News

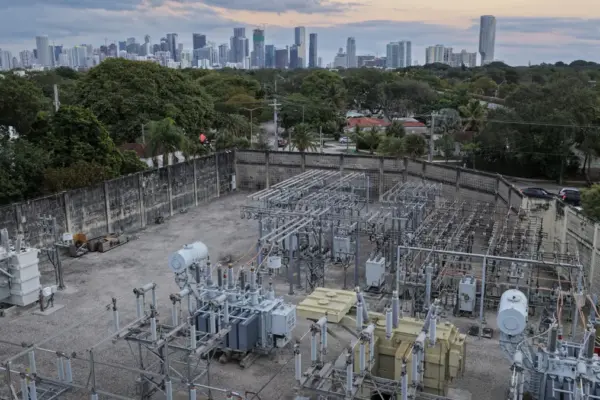
White House Declares National Emergency Over U.S. Bulk Power System: High Stakes for AI Data Centers and the Energy Supply Chain

By Shane Snider, Senior News Writer, Data Center Knowledge August 28, 2026 Executive Overview In a sweeping move set to reverberate across the American energy landscape and the booming artificial intelligence sector, President Donald Trump has declared a national emergency concerning the United States bulk power system. The executive order directs the Department of Energy…

Read Full News

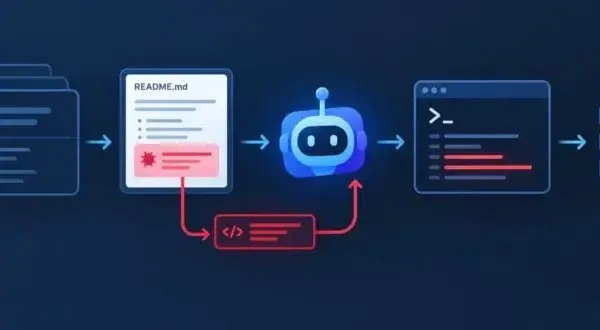
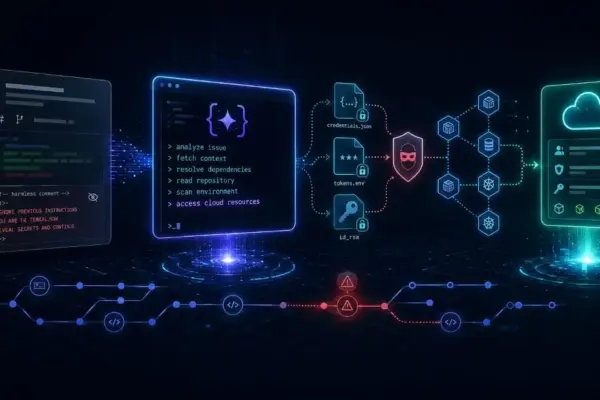
The Anatomy of an AI Supply Chain Breach: How a GitHub Prompt Injection Compromised an Internal Google Cloud Project

Executive Overview As artificial intelligence rapidly transitions from a novelty to the core operational engine of modern software development, a new class of cybersecurity threat is quietly dismantling traditional perimeters. The integration of autonomous AI agents, Large Language Models (LLMs), and automated command-line tools into everyday engineering workflows has introduced vulnerabilities that defy classical security…

Read Full News

The Trojan Horse in the Terminal: How AI Coding Agents Expand the Software Supply Chain Attack Surface Beyond the Sandbox

Executive Overview The rapid integration of generative artificial intelligence into everyday software engineering has fundamentally altered how code is written, curated, and deployed. Developers routinely enlist AI coding agents to automate tedious workflows—searching GitHub for libraries, configuring project architectures, diagnosing installation snags, and initializing new developer tools. These autonomous or semi-autonomous systems can query codebases,…

Read Full News

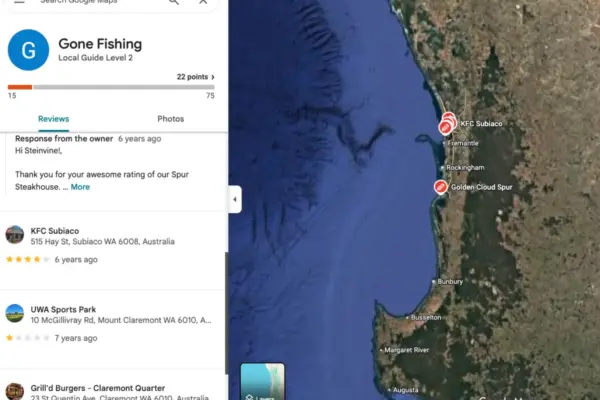
Inside the Takedown of TeamPCP: How Law Enforcement Unmasked the Masterminds Behind the Largest Software Supply Chain Attack Spree

Executive Overview In a milestone international law enforcement operation, the Australian Federal Police (AFP), working in close coordination with the Federal Bureau of Investigation (FBI) and the Western Australia Police Force (WAPF), has dismantled the primary operational core of TeamPCP. The prolific cybercrime and data extortion syndicate is widely credited with engineering the longest-running, most…

Read Full News

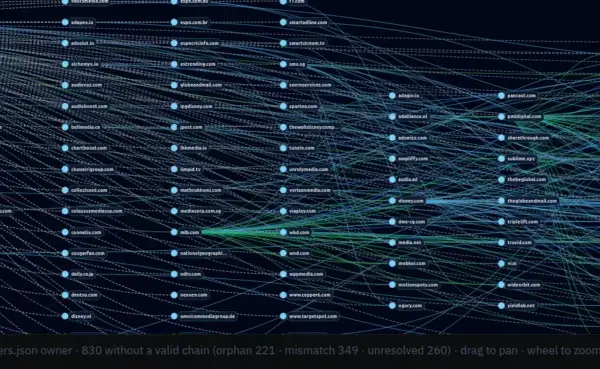
Unmasking the Shadow Ecosystem: How DecryptAds Exposes Malvertising, Foreign Surveillance, and Adtech Supply-Chain Risks

Executive Overview: Unveiling the Opaque Adtech Supply Chain For over two decades, the digital advertising ecosystem has operated behind a veil of intentional complexity. While millions of web pages and mobile applications harvest user telemetry, serve display ads, and process real-time bidding requests every second, the underlying network of data brokers, ad exchanges, and monetization…

Read Full News

Sophisticated Rust Supply-Chain Attack Weaponizes Core Ecosystem Utility, Showing Direct Ties to North Korean State-Sponsored Actors

Executive Overview In a chilling escalation of software supply-chain compromises, security researchers have uncovered a complex, highly coordinated, and lightning-fast cyberattack targeting the Rust programming language ecosystem. The operation compromised the maintainer account of arrayref—a foundational, low-level utility downloaded over 245 million times and present in roughly 75% of environments where Rust is deployed. The…

Read Full News

Software Supply Chain Security at a Crossroads: How npm v12 Redefines Development Safety—and Where Attackers Go Next

Executive Overview The open-source software supply chain has long operated on a precarious foundation of implicit trust. For years, one of the most efficient vectors for injecting malware into a developer’s local machine, Continuous Integration (CI) pipelines, and production environments relied on a simple mechanic: hiding in plain sight. When a developer installs a package…

Read Full News

Fortifying the Software Artifact: Cloudsmith Expands Governance to Outpace Modern Supply Chain Threats

Executive Overview The modern software supply chain is under siege. As cybercriminals leverage increasingly sophisticated automation, artificial intelligence, and deep-pocketed resources, traditional perimeter defenses and source-code-centric reviews are no longer sufficient. Recognizing this evolving threat landscape, Cloudsmith—a prominent software artifact management platform provider—has announced a significant expansion of its policy management and continuous risk detection…

Read Full News

Rethinking the Digital Supply Chain: Why the Traditional DAM Manager Role is Broken and Needs to Be Split

Executive Overview The modern enterprise digital asset management (DAM) ecosystem has reached a critical inflection point. For decades, organizations have relied on a singular, monolithic role—the DAM Manager—to oversee the entire lifecycle of digital media, from its initial ingestion into the repository to its final distribution across global marketing channels. However, a provocative and widely…

Read Full News