Beyond the "Nine Nines": Why Modern Mainframe Resilience Demands a Cloud-Driven Paradigm Shift

Executive Overview For decades, the enterprise mainframe has occupied a singular position in the corporate technology hierarchy: the untouchable bastion of reliability. Renowned for its fault-tolerant hardware, built-in redundancy, and instantaneous automatic recovery, the platform has long delivered what systems architects colloquially refer to as "nine nines" of availability—translating to a mere 31.56 milliseconds of…
Read Full News

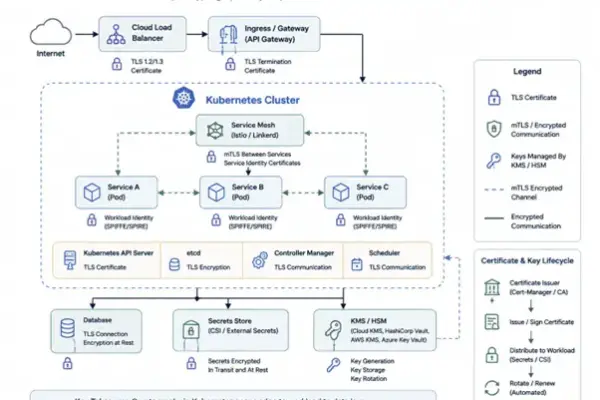
Beyond the Algorithm Swap: Why DevOps Must Master Cryptographic Inventories for the Post-Quantum Era

Executive Overview For years, the conversation surrounding post-quantum cryptography (PQC) has suffered from tunnel vision. Industry discourse inevitably races past complex integration challenges, homing in instead on a straightforward algorithm-replacement exercise. Stakeholders quickly pivot to debating the merits of RSA, Elliptic Curve Cryptography (ECC), ML-KEM, digital signatures, and hybrid key exchanges—obsessing over which mathematical formulas…

Read Full News

Software Supply Chain Security at a Crossroads: How npm v12 Redefines Development Safety—and Where Attackers Go Next

Executive Overview The open-source software supply chain has long operated on a precarious foundation of implicit trust. For years, one of the most efficient vectors for injecting malware into a developer’s local machine, Continuous Integration (CI) pipelines, and production environments relied on a simple mechanic: hiding in plain sight. When a developer installs a package…

Read Full News

Navigating the AI Gold Rush in DevOps: Beyond the Hype to Measurable Engineering Value

Executive Overview The DevOps community is no stranger to technological extremes. Not too long ago, the industry marched to the ubiquitous mantra of "Automate Everything." Automation was hailed as a universal panacea capable of curing any engineering bottleneck, squashing deployment friction, and turning sluggish legacy workflows into hyper-efficient pipelines. Over time, however, the industry arrived…

Read Full News

Beyond the SDK: The Hidden Labor and Evolving Architecture of OpenTelemetry Deployments

EXECUTIVE OVERVIEW For years, the application performance monitoring (APM) market was defined by vendor lock-in. Engineering teams seeking deep visibility into distributed systems were forced to integrate proprietary agents deeply into their codebase. Switching APM vendors required a monumental, high-risk re-instrumentation effort, effectively binding an organization’s operational insights to a single commercial ecosystem. The advent…

Read Full News

The End of the Honeymoon: Anthropic Rolls Back Claude Code Limits and Exposes the AI Subscription Dilemma

Executive Overview For heavy users and automated development teams relying on Anthropic’s flagship coding assistant, the era of unconstrained, promotional headroom is officially drawing to a close. Tonight at 11:59 PM PT, Anthropic’s temporary 50% bump to Claude Code’s weekly usage limits will expire. This marks the fourth deadline Anthropic has set for this specific…

Read Full News

Bridging the Release Gap: How Hybrid Automation and Software Testing Principles Are Reshaping IT Infrastructure

Executive Overview The rapid democratization of software development—accelerated heavily by generative artificial intelligence and agentic code generation—has created an unprecedented bottleneck in enterprise technology: the Release Gap. While AI-driven tooling has made code cheap, fast, and remarkably abundant, the traditional mechanisms used to validate, regression-test, and deploy these applications have failed to keep pace. Enterprises…

Read Full News

Fortifying the Software Artifact: Cloudsmith Expands Governance to Outpace Modern Supply Chain Threats

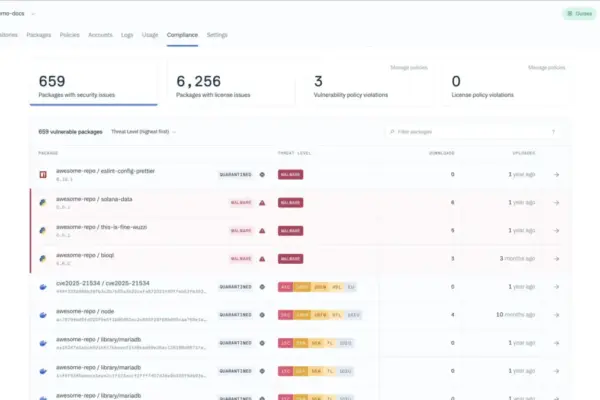
Executive Overview The modern software supply chain is under siege. As cybercriminals leverage increasingly sophisticated automation, artificial intelligence, and deep-pocketed resources, traditional perimeter defenses and source-code-centric reviews are no longer sufficient. Recognizing this evolving threat landscape, Cloudsmith—a prominent software artifact management platform provider—has announced a significant expansion of its policy management and continuous risk detection…

Read Full News

Global Development Stalled: Examining the Scale, Impact, and Vulnerabilities Behind GitHub’s Major Monday Outage

Executive Overview On a Monday morning that quickly descended into chaos for engineering organizations across the globe, a catastrophic technical outage paralyzed GitHub, the world’s largest source code hosting and collaboration platform. For several critical hours, the Microsoft-owned service—which underpins the daily workflows of approximately 180 million developers worldwide—experienced severe degradation and unprecedented error rates….

Read Full News

The Hidden Ledger of DevSecOps: Quantifying the True Delivery Cost of Pipeline Security

Executive Overview For the better years of the modern software engineering lifecycle, the industry mantra has been absolute and unwavering: "Shift left." The core philosophy is elegantly straightforward—catch security vulnerabilities earlier in the development lifecycle, fix them when they are cheapest to remediate, and build a more resilient product by baking safety directly into the…

Read Full News