Executive Overview
The global cybersecurity landscape has crossed a critical threshold. A comprehensive new vulnerability backlog analysis released by HackerOne reveals a startling paradox at the heart of modern software security: while enterprise security and DevSecOps teams have dramatically accelerated their remediation workflows, they are rapidly losing ground to an unprecedented deluge of software vulnerabilities.
According to the data, organizations have successfully slashed their average vulnerability resolution time from a sluggish 135 days down to just 62 days over the past year—representing a commendable 54% efficiency boost in remediation velocity. However, this operational improvement has been completely eclipsed by a staggering 131% surge over the last two years in the total volume of known, validated security issues sitting unresolved in enterprise backlogs.
This widening chasm between vulnerability discovery and remediation is primarily driven by the rapid, widespread integration of artificial intelligence (AI) across both offensive and defensive cybersecurity domains. Security researchers and malicious threat actors alike are weaponizing generative AI and automated code-analysis tools to unearth software flaws at a scale and speed previously thought impossible. Concurrently, software developers are leaning heavily on AI coding assistants to accelerate application delivery, inadvertently injecting novel classes of AI-specific architectural flaws into corporate codebases.
The consequences for enterprise risk management are profound. Historically, DevSecOps teams operated under a comfortable safety buffer—a temporal window lasting weeks or months between the public disclosure of a software flaw and the operationalization of a functional exploit by cybercriminals. Today, that luxury has vanished. Driven by automated reverse-engineering pipelines powered by machine learning, sophisticated threat actors can now analyze a newly discovered vulnerability, construct a working exploit, and launch targeted attacks within a matter of hours.
As corporate exposure debt reaches historic highs—higher than at any point in HackerOne’s decade-long reporting history—industry leaders are issuing urgent warnings. Organizations must fundamentally rethink their security economics, moving away from a reactive posture focused solely on feature velocity and embracing automated vulnerability operations (VulnOps) to survive the AI-driven threat landscape.
Detailed Chronology: The Escalating Dynamics of the Vulnerability Backlog
To understand the current crisis, one must trace the evolutionary trajectory of vulnerability discovery and remediation over the past several years. For decades, the equilibrium of application security (AppSec) relied on a linear relationship: software was written by humans, tested by humans, and audited by human security researchers. Vulnerabilities were discovered at a manageable, incremental rate, allowing internal security teams to triage, patch, and deploy fixes without experiencing catastrophic burnout.
The Shift Toward AI-Accelerated Discovery (2024–2025)
The inflection point arrived with the mainstream democratization of large language models (LLMs) and specialized code-auditing AI agents. By late 2024, ethical hackers and independent security researchers began aggressively integrating AI tooling into their reconnaissance and testing workflows.
A specialized HackerOne survey of 408 active security researchers highlights this profound transformation: 85% of respondents reported that they are actively upskilling and conducting vulnerability research using artificial intelligence. Nearly three-quarters (73%) of these researchers noted a meaningful, measurable increase in the volume of valid, high-impact security findings they were able to uncover. Furthermore, armed with AI capabilities, 68% of surveyed researchers reported a strategic shift away from low-level, routine bugs toward higher-complexity, higher-bounty vulnerabilities that require deep logical analysis—tasks that AI excels at accelerating.
This paradigm shift is starkly reflected in platform payouts. HackerOne reported that organizations running bug bounty programs on its platform distributed a record-breaking $89 million to security researchers between July 2025 and June 2026. This figure represents an 18% increase over the previous year, setting an all-time high in the platform’s history and underscoring the sheer volume of high-severity flaws being successfully identified.
The DevSecOps Bottleneck (2025–2026)
While researchers unlocked unprecedented efficiency through AI, enterprise DevSecOps teams found themselves facing an insurmountable operational bottleneck. A secondary survey of 111 enterprise security leaders revealed that 70% of organizations are currently seeing validated security findings added to their remediation backlogs at a rate far faster than their engineering teams can clear them.
Even though organizations demonstrated an impressive ability to cut average resolution times from 135 days down to 62 days, the sheer volume of incoming reports overwhelmed human triage systems. The math simply does not favor traditional remediation pipelines. When a single security researcher can leverage AI to generate dozens of complex, valid vulnerability reports in the time it once took to manually discover one, the downstream engineering effort required to patch, test, and deploy code updates creates a permanent backlog state.
The Compression of the Exploit Lifecycle
Perhaps the most alarming development in this chronology is the dramatic compression of the exploit lifecycle. Historically, enterprise risk managers could prioritize patching based on theoretical exploitability and the time it would take an adversary to reverse-engineer a patch or a disclosure advisory.
In the current threat environment, that window has collapsed. Cybercriminals are equally adept at deploying AI to automate the discovery and weaponization of zero-day and newly disclosed vulnerabilities. In numerous documented instances, malicious actors have utilized machine learning models to reverse-engineer a patch or an advisory, creating a functional exploit in a matter of hours rather than months. This dynamic turns exposure management into a breathless, real-time race against time where a delayed patch no longer represents a minor compliance oversight, but an open invitation to immediate compromise.
Supporting Context & Metrics: The Anatomy of Modern Exposure Debt
The empirical data compiled in HackerOne’s latest analysis paints a vivid picture of an industry grappling with structural exposure debt.
The Metrics of the Crisis
- The 131% Surge: Over the past two years, the total aggregate number of known, validated, and unresolved security issues sitting in enterprise backlogs has escalated by 131%.
- The Remediation Speedup: Organizations have successfully decreased their average resolution timeline from 135 days to 62 days, reflecting a 54% improvement in remediation velocity.
- The Influx Ratio: 70% of security leaders report that validated findings are entering their backlogs faster than they can be remediated.
- The Financial Scale: Bug bounty payouts on the HackerOne platform reached an all-time high of $89 million between July 2025 and June 2026—an 18% year-over-year increase.
- The Upskilling Wave: 85% of security researchers are actively utilizing AI to enhance their vulnerability discovery workflows, with 68% pivoting toward high-complexity bugs.
The Rise of AI-Specific Application Vulnerabilities
Compounding the volume issue is the changing nature of the code itself. As mainstream application developers rapidly adopt generative AI tools to write software, they are inadvertently introducing entirely new categories of security weaknesses that traditional static analysis tools (SAST) and dynamic testing tools (DAST) were never designed to catch.
According to HackerOne’s telemetry, enterprises are contending with unprecedented spikes in AI-specific architectural flaws:
- System Prompt Leakage: A massive 557% increase in reports detailing system prompt leakage, where users manipulate LLM-powered applications to reveal proprietary underlying instructions, system constraints, and sensitive backend logic.
- Output Handling Failures: A 264% increase in output handling vulnerabilities, where applications fail to properly sanitize, validate, or contextualize the responses generated by AI models before executing them or presenting them to end users, opening the door to advanced injection attacks.
Tracking vs. Eliminating Exposure Debt
On a positive note, enterprise awareness of this challenge is maturing. Three-quarters (75%) of surveyed security leaders report that their organizations now formally track "exposure debt"—the cumulative risk represented by unresolved security backlogs—as a core operational metric.
However, tracking a problem is vastly different from solving it. While security teams are better at measuring their vulnerability debt, they are struggling to secure the engineering resources necessary to pay it down. In the decade that HackerOne has published its annual application security assessments, the overall level of enterprise exposure debt has never been higher.
Official Statements and Industry Insights
Industry executives and security leaders emphasize that incremental improvements to existing processes will no longer suffice. The structural mismatch between software creation, vulnerability discovery, and remediation demands a fundamental modernization of enterprise security strategy.
Kara Sprague, CEO of HackerOne, highlighted the urgency of the current moment during the release of the findings:
"As researchers make use of AI to discover vulnerabilities, it’s apparent that DevSecOps teams are starting to be overwhelmed. As a result, it’s clear that many of those teams now need to start applying AI to remediate vulnerabilities faster by, for example, formally addressing best vulnerability operations (VulnOps) practices."
Sprague pointed out a persistent cultural and financial misalignment within corporate boardrooms. Despite mounting security pressures, far too many organizations continue to allocate the vast majority of their application development budgets and engineering hours toward building new features and launching new applications, starving the security and remediation functions of the resources they desperately need.
"In the 10 years that HackerOne has been sharing its application security reports, the overall level of exposure debt has never been higher," Sprague noted. "Unfortunately, it usually requires some actual crisis before an organization revisits its DevSecOps strategy."
Security analysts echo these sentiments, noting that organizations often treat application security as an afterthought or a compliance checkbox rather than an integrated component of software engineering lifecycle (SDLC) economics. Without a concerted shift toward automated VulnOps and proactive debt reduction, enterprises will continue running faster just to stay in the same place.
Future Outlook: Navigating the AI Security Horizon
Looking ahead, the trajectory of application security will depend entirely on how swiftly enterprise DevSecOps teams can adopt artificial intelligence as a defensive force multiplier.
Embracing Automated VulnOps
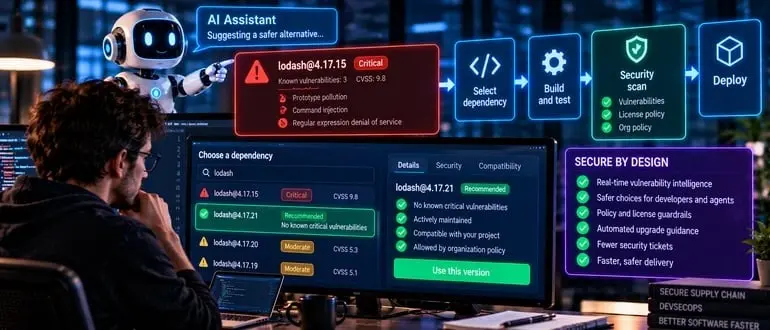
To survive the incoming wave of AI-discovered vulnerabilities, organizations must institutionalize vulnerability operations (VulnOps) as a distinct, automated discipline. Just as Site Reliability Engineering (SRE) transformed infrastructure management through automation and observability, VulnOps must leverage AI-driven remediation engines to automatically triage, test, and deploy patches for routine and medium-severity vulnerabilities without requiring manual human intervention for every single line of code.
Redefining Engineering Priorities
Boardrooms and executive leadership teams must reconcile feature velocity with security debt. Continuing to prioritize rapid application delivery at the expense of vulnerability remediation is a financially unsustainable gamble. As the window between vulnerability disclosure and active exploitation shrinks to mere hours, accumulated exposure debt transforms from a manageable technical backlog into an existential business risk.
The Proactive Imperative
Ultimately, the cybersecurity industry remains locked in an eternal race between offense and defense. While the number of discovered vulnerabilities has climbed exponentially, it remains an open question whether this surge will translate into a corresponding, one-to-one increase in enterprise breaches—largely due to the heroic efforts of under-resourced security teams working around the clock.
However, relying on organizational resilience in the face of escalating adversary capabilities is a flawed strategy. As the old adage in risk management dictates: an ounce of DevSecOps prevention and automated remediation is worth a pound of incident management applied long after the damage has already been done. Enterprises that fail to harness AI for remediation today risk becoming the next headline in tomorrow’s breach logs.
Frequently Asked Questions (FAQ)
Why is vulnerability debt still growing if teams are fixing issues faster?
While organizations have improved their average remediation speed (cutting resolution time from 135 to 62 days), the rate at which vulnerabilities are being discovered is accelerating even faster. The adoption of AI tools by security researchers and malicious actors has led to a massive influx of validated findings, outpacing the engineering capacity of enterprise DevSecOps teams.
What is exposure debt?
Exposure debt refers to the accumulated backlog of validated vulnerabilities, security weaknesses, and architectural flaws that remain unresolved across an organization’s software portfolio over time. Much like technical debt, it represents mounting risk that must eventually be paid down.
How can DevSecOps teams respond to this crisis?
DevSecOps teams can combat surging exposure debt by implementing automated vulnerability operations (VulnOps) practices, utilizing AI-assisted remediation tools to patch code faster, prioritizing high-impact exposures, and establishing exposure debt as a formal, trackable operational metric at the executive level.
What are AI-specific vulnerabilities, and why are they increasing?
As application developers use generative AI to write code, organizations are seeing dramatic spikes in novel architectural flaws—such as a 557% increase in system prompt leakage reports and a 264% increase in output handling errors. These vulnerabilities stem from the unique security challenges of integrating large language models into software applications.