The Artificial Intelligence Arms Race: How Surging Vulnerability Backlogs and AI-Driven Exploits Are Overwhelming DevSecOps Teams

Executive Overview The global cybersecurity landscape has crossed a critical threshold. A comprehensive new vulnerability backlog analysis released by HackerOne reveals a startling paradox at the heart of modern software security: while enterprise security and DevSecOps teams have dramatically accelerated their remediation workflows, they are rapidly losing ground to an unprecedented deluge of software vulnerabilities….
Read Full News

Navigating the Release-Day Crunch: How DevSecOps Integration Eradicates the Final Security Gate Bottleneck

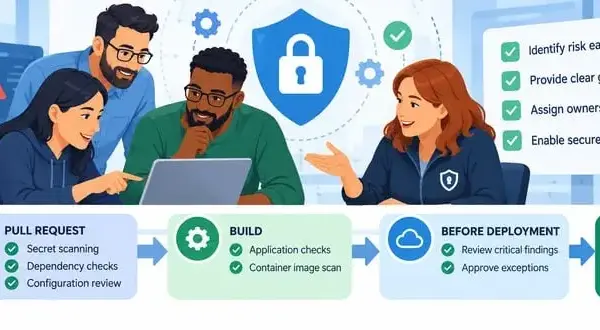
Executive Overview The scene is agonizingly familiar across software engineering organizations worldwide: mere hours before a major product release, a routine automated dependency scan flashes a critical warning. A newly flagged library vulnerability threatens to derail months of hard work. The development team scrambles to formulate a solution, only to realize that applying the immediate…

Read Full News

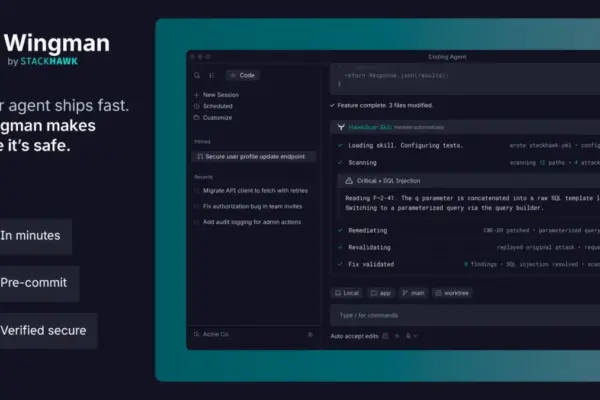
StackHawk’s Wingman Redefines DevSecOps: Automated Vulnerability Remediation Hits the AI Coding Loop

Executive Overview The rapid acceleration of software development driven by artificial intelligence has unlocked unprecedented levels of developer productivity, but it has simultaneously exacerbated a sprawling crisis in application security. As millions of developers routinely turn to AI coding assistants to generate complex routines, the volume of code moving from ideation to production has completely…

Read Full News

The Death of Source Code: How the Rise of Autonomous AI Agents is Forcing DevSecOps to Shift from Code to Binaries

Executive Overview The fundamental premise of software engineering—that human developers write, review, and maintain lines of source code—is facing an existential reckoning. Speaking before a packed auditorium of approximately 500 software engineers and industry leaders at the swampUP 2026 conference, JFrog CEO Shlomi Ben Haim delivered a provocative yet pragmatic thesis: in the rapidly approaching…

Read Full News

The Hidden Ledger of DevSecOps: Quantifying the True Delivery Cost of Pipeline Security

Executive Overview For the better years of the modern software engineering lifecycle, the industry mantra has been absolute and unwavering: "Shift left." The core philosophy is elegantly straightforward—catch security vulnerabilities earlier in the development lifecycle, fix them when they are cheapest to remediate, and build a more resilient product by baking safety directly into the…

Read Full News

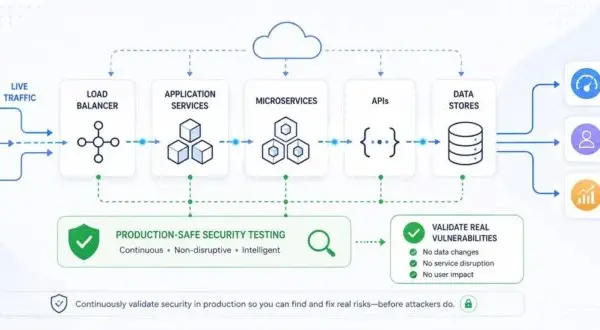
Bridging the DevSecOps Blind Spot: Why Production-Safe Testing is the Frontier of Modern Cyber Defense

Executive Overview For over a decade, the core tenet of application security has been "shift-left." Organizations have poured unprecedented capital, engineering hours, and tooling into pre-deployment pipelines—scanning source code, running static and dynamic application security testing (SAST/DAST), and auditing container images long before a single line of code reaches end users. Yet, despite these rigorous…

Read Full News