Executive Overview
The rapid democratization of generative artificial intelligence and the proliferation of autonomous coding agents have created an unprecedented paradigm shift in software development. While these advanced tools promise exponential gains in developer productivity, they have simultaneously introduced a severe logistical bottleneck for the cloud-based platforms that host modern codebases.
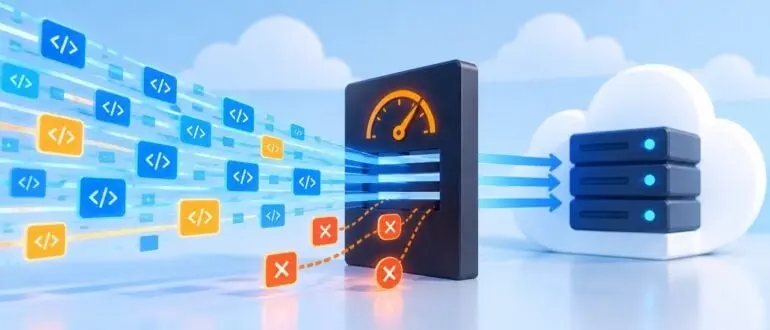
In a decisive move to safeguard its underlying architecture from infrastructural exhaustion, DevOps giant GitLab has announced the implementation of strict new rate limits across its flagship cloud-based platform, GitLab.com. Driven by an exponential surge in automated workloads, continuous integration pipelines, and AI-powered coding assistants that endlessly ping servers, these policy shifts represent a crucial turning point in how developer ecosystems manage finite compute resources.
Beginning October 19, the platform will systematically restrict the volume of requests that users can execute, calibrated directly to their subscription tier. While Free-tier users and unauthenticated automated scripts will bear the immediate brunt of these regulations, enterprise-grade Premium and Ultimate subscribers have been granted a longer runway, with enforcement for their tiers deferred until January 2027.
This policy change is far from an isolated corporate maneuver. It underscores an industry-wide reckoning: major developer hubs, including GitHub and AI infrastructure providers like Anthropic, are actively scrambling to recalibrate their infrastructure limits. As autonomous agents continuously query repositories, run automated tests, and synchronize assets at machine speeds, the foundational networks of the global software supply chain are beginning to strain under the weight of the AI revolution.
Detailed Chronology and Implementation Roadmap
To ensure a smooth transition and mitigate widespread disruptions to active continuous integration and continuous deployment (CI/CD) pipelines, GitLab has laid out a phased rollout schedule. This methodical timeline is designed to give development teams ample opportunity to audit their automation scripts, implement proper authentication protocols, and refactor applications that rely heavily on frequent API polling.
The October Rollout and Testing Windows
The initial wave of restrictions goes live on October 19. However, prior to permanent enforcement, GitLab has scheduled two critical, high-visibility stress-testing windows:
- October 7: A four-hour live simulation from 8:00 AM to 12:00 PM Pacific Time.
- October 14: A second four-hour stress test operating during the same morning window.
During these designated trials, all Free-tier and unauthenticated traffic will be strictly subjected to the new thresholds. GitLab has strongly encouraged developers and enterprise administrators to monitor their applications during these operational windows. By doing so, engineering teams can proactively identify bottlenecks, spot unauthenticated API calls originating from legacy scripts, and adjust their tooling before the restrictions become permanent.
Phased Tiers and Future Deadlines
The enforcement timeline is intentionally tiered to prioritize smaller accounts while granting enterprise customers sufficient time to scale or adapt their automated architectures:
- October 19, 2023 (or current rollout schedule): Unauthenticated requests and Free-tier accounts face immediate caps. Anonymous traffic is capped at a strict 60 requests per hour per IP address, while authenticated Free users receive 5,000 requests per hour.
- January 2027: Premium and Ultimate subscribers will transition into their respective rate-limiting frameworks, granting them higher hourly and per-minute allowances tailored for enterprise-scale automation.
Crucially, these changes apply exclusively to GitLab.com. Organizations managing their own infrastructure via GitLab Self-Managed or GitLab Dedicated will retain autonomous control over their local rate-limiting configurations, insulating internal corporate networks from these public cloud constraints.
Supporting Context & Metrics: The Mechanics of Machine-Generated Traffic
To fully understand why GitLab is overhauling its rate-limiting policies, one must examine the staggering metrics governing modern software development. Traditional software engineering was fundamentally human-driven: developers wrote code, committed changes manually, and pulled repositories a few dozen times a day. Today, autonomous AI agents—ranging from customized Large Language Model (LLM) wrappers to sophisticated integrated development environment (IDE) assistants—interact with code repositories at volumes that human developers simply cannot match.
Quantifying the Limits
Under the newly minted policy framework, GitLab has established distinct request allowances across all subscription levels, covering API traffic, standard web requests, and authenticated Git operations conducted over HTTPS:
| Subscription Tier | Hourly Request Limit | Per-Minute Burst Limit | Unauthenticated IP Limit |
|---|---|---|---|
| Unauthenticated / Anonymous | 60 requests / hour | N/A | 60 requests / hour |
| Free Tier | 5,000 requests / hour | 100 requests / minute | N/A |
| Premium Tier | 15,000 requests / hour | 1,250 requests / minute | N/A |
| Ultimate Tier | 25,000 requests / hour | 2,000 requests / minute | N/A |
The inclusion of per-minute burst limits is particularly vital. These thresholds are explicitly engineered to accommodate short, intense bursts of programmatic activity—such as when a massive test suite runs or an AI agent rapidly indexes a repository—without instantly locking out the user.
The Pitfall of Unauthenticated Automation
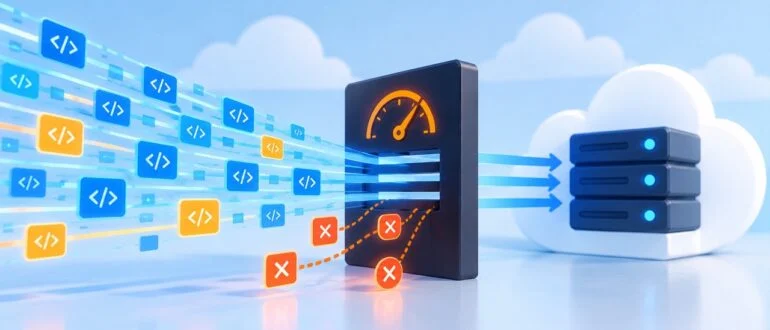
One of the most insidious technical traps for development teams utilizing AI tools is accidental unauthenticated traffic. GitLab’s policy dictates that the strict 60-request-per-hour anonymous limit applies based entirely on whether valid credentials are supplied. If an enterprise-grade organization running an Ultimate subscription deploys an internal AI agent or automation script that fails to properly pass credentials (such as personal access tokens or OAuth tokens), that traffic is instantly categorized as anonymous.
Consequently, even multi-million-dollar enterprise accounts can find their internal tooling throttled if poorly configured scripts make rapid, unauthenticated calls against the GitLab.com API.
Official Statements and Industry-Wide Implications
Industry analysts view GitLab’s policy shift as a harbinger for the broader technology sector. As generative AI models transition from experimental novelties to mission-critical enterprise workflows, the underlying infrastructure costs are forcing platform architects to rethink the traditional "all-you-can-eat" access models that defined the cloud era.
Mitigating the Strain on Shared Infrastructure
In internal analyses shared with enterprise clients, GitLab noted that while internal stress testing reveals that nearly all everyday human users operate well below these new thresholds, a small minority of heavy automation scripts and Free-tier accounts consume a disproportionate percentage of available server bandwidth. GitLab forecasts that overall platform traffic could multiply several times over across the coming years, driven almost entirely by automated machine agents.
"Maintaining high availability, low latency, and robust platform security requires us to establish predictable guardrails," notes telemetry data from developer operations circles. Without these interventions, cascading API loops generated by runaway AI agents risk destabilizing shared cloud environments for all users.
The Broader Tech Landscape
GitLab is far from alone in constructing defensive barriers against the AI traffic tsunami.
- GitHub, the world’s largest code repository hosting service, has increasingly tightened its abuse detection and secondary rate-limiting algorithms to curb scraping and automated bot behavior.
- Anthropic, OpenAI, and other foundational AI model providers have long enforced aggressive rate limits and token-per-minute (TPM) caps to manage compute clusters dominated by automated enterprise workflows.
The consensus across the software engineering community is clear: the era of boundless, unrestricted API access is rapidly drawing to a close, replaced by a nuanced economy of compute quotas and tiered rate management.
Future Outlook: Adapting to the New Rate-Limited Reality
For software engineering teams, adapting to GitLab’s new regime requires a proactive shift in how applications, CI/CD pipelines, and AI integrations are architected. Waiting until an application returns an HTTP 429 (Too Many Requests) status code is no longer an acceptable operational strategy.
Developer Tooling and Monitoring
To assist developers in navigating these changes ahead of the January 2027 enterprise enforcement and the immediate October 2023/2024 rollouts, GitLab is rolling out several transparency and mitigation features:
- Usage Dashboards: The platform is actively developing an integrated user interface designed to display real-time customer usage metrics against assigned plan limits.
- Header Telemetry: Until the dedicated UI dashboard is fully deployed, developers can programmatically monitor their consumption by inspecting the
RateLimit-Remainingheader included in standard API responses. - Graceful Handling: When limits are exceeded, GitLab returns an
HTTP 429response accompanied by aRetry-Afterheader, indicating the exact timestamp when applications are cleared to resume sending requests.
Architectural Best Practices for AI Workloads
Engineering teams deploying autonomous agents or heavy CI/CD integrations must adopt robust optimization strategies to avoid slamming into these structural ceilings:
- Aggressive Caching: Frequently requested repository data, metadata, and static assets should be cached locally to minimize redundant network calls.
- Batching Operations: Rather than executing hundreds of micro-requests to update issues or merge requests, scripts should leverage bulk API endpoints where available.
- Eliminating Polling: Developers should transition away from active polling scripts and instead rely on webhook-driven architectures that notify systems only when state changes actually occur.
- Proper Authentication: Guaranteeing that every script, bot, and AI agent securely passes personal access tokens, OAuth tokens, or CI/CD job tokens ensures traffic is appropriately routed to the higher tiers associated with paid subscriptions.
Paid Capacity Extensions on the Horizon
Recognizing that legitimate enterprise workloads may occasionally outgrow even the generous 25,000-request-per-hour Ultimate tier, GitLab has confirmed that it is actively developing a mechanism for customers to purchase additional request allowances beyond standard subscription ceilings. Further details regarding this commercial overage model are expected to be unveiled later this year.
As the software development lifecycle becomes increasingly intertwined with artificial intelligence, GitLab’s calculated approach to rate limiting establishes a vital blueprint for balancing infrastructural sustainability with the relentless, automated demands of tomorrow’s programmers.