U.S. Federal Register’s Brief Deployment of Alibaba AI Sparks National Security Debate and Highlights U.S. Open-Source Vulnerabilities

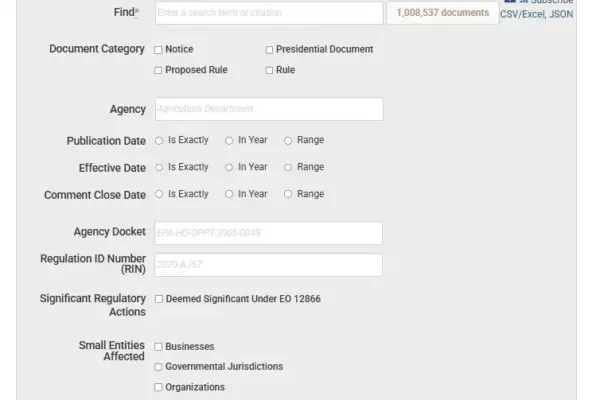
Executive Overview In a striking revelation that underscores the complex and rapidly evolving geopolitical landscape of artificial intelligence, U.S. government officials abruptly removed a Chinese-developed AI search tool from the official Federal Register website. The tool, powered by an open-weight model from Alibaba’s Qwen family, was quietly deployed to help users navigate public comments on…
Read Full News

International Meteor Organization Crippled by Devastating Cyberattack, Exposing Vulnerabilities in Scientific Non-Profit Infrastructure

Executive Overview In a stunning digital assault that has sent shockwaves through the global astronomical community, the International Meteor Organization (IMO)—a premier non-profit body coordinating both amateur and professional meteor observations worldwide—has fallen victim to a debilitating cyberattack. The breach, which struck earlier this week, has rendered large portions of the organization’s core digital infrastructure…

Read Full News

Critical GitLab Vulnerabilities Spark Urgent Industry Wake-Up Call Over "Calendar-Speed" Patching

Executive Overview In the fast-paced ecosystem of modern software development, enterprise trust often rests on a single foundational pillar: the security of the DevOps pipeline. This week, that trust faced a severe stress test. GitLab administrators worldwide received an unwelcome and alarming reminder that a single, poorly guarded API endpoint can instantly dismantle years of…

Read Full News

The Silent Supply Chain Heist: Active Exploitation of JFrog Artifactory Vulnerabilities Exposes Dangerous Gaps in Build Infrastructure Security

Executive Overview Artifact repositories occupy a strange, often misunderstood blind spot within modern enterprise security architectures. Unlike outward-facing web applications, they rarely front the public internet directly. Unlike hardened production databases, they do not hold raw customer Personally Identifiable Information (PII) or credit card repositories. Yet, these platforms harbor assets that are arguably far more…

Read Full News

Securing the Digital Frontier: Senator Wyden Pressures NSA for Comprehensive Public Guidance on VPN Vulnerabilities and Best Practices

WASHINGTON — In an era defined by aggressive state-sponsored cyber espionage, digital privacy tools have transformed from niche software into vital armor for journalists, dissidents, defense contractors, and everyday citizens. Yet, millions of internet users who rely on Virtual Private Networks (VPNs) to shield their data from foreign adversaries may be operating under a false…

Read Full News

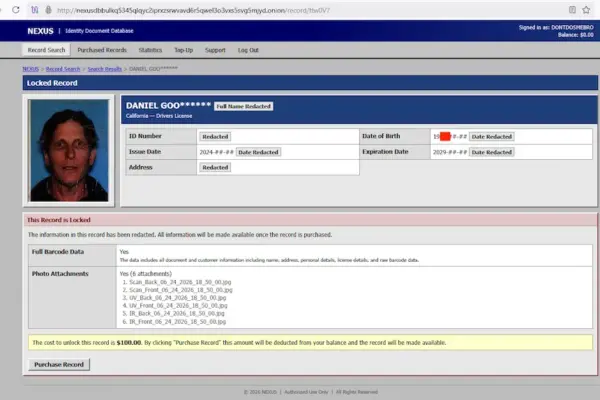
INVESTIGATIVE REPORT: The Nexus Breach Exposes Vulnerabilities in Third-Party ID Scanning and Real-Time Data Harvesting

Executive Overview In the modern digital economy, the friction of daily life has been largely streamlined through biometric and document-based verification. Whether checking into a hotel, renting a vehicle for a weekend getaway, or entering a regulated establishment, handing over a driver’s license or state-issued identification card has become an almost mindless routine. Consumers are…

Read Full News

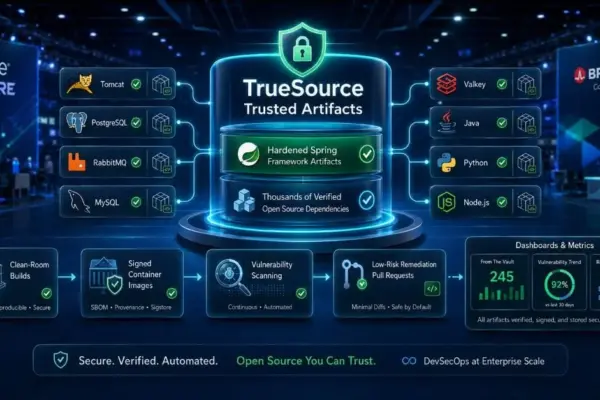
Securing the Enterprise Software Supply Chain: Broadcom Launches TrueSource at VMware Explore to Combat the AI-Driven Surge in Vulnerabilities

Executive Overview At the VMware Explore conference, Broadcom made a landmark announcement aimed at transforming how modern enterprises manage, secure, and deploy open-source software. The company unveiled TrueSource Trusted Artifacts by Broadcom, an expansive suite of hardened libraries and container images designed specifically for the widely used open-source Spring framework, along with the 5,000 vital…

Read Full News

Regulatory Crackdown: Roblox Faces Mandatory Independent Audits in Australia Over Child Safety and Grooming Vulnerabilities

Executive Overview Roblox, one of the world’s most popular online gaming and user-generated content platforms, has become the first digital platform of its kind to submit to court-enforceable, independent third-party audits under Australia’s landmark Online Safety Act. This decisive regulatory intervention follows a rigorous investigation by Australia’s eSafety Commissioner, Julie Inman Grant, which revealed glaring…

Read Full News

Global Development Stalled: Examining the Scale, Impact, and Vulnerabilities Behind GitHub’s Major Monday Outage

Executive Overview On a Monday morning that quickly descended into chaos for engineering organizations across the globe, a catastrophic technical outage paralyzed GitHub, the world’s largest source code hosting and collaboration platform. For several critical hours, the Microsoft-owned service—which underpins the daily workflows of approximately 180 million developers worldwide—experienced severe degradation and unprecedented error rates….

Read Full News

Artificial Intelligence Triggers Unprecedented Patch Avalanche: Microsoft Fixes Over 570 Vulnerabilities in Historic Security Release

Executive Overview The global cybersecurity ecosystem has crossed an operational threshold. In a security release that fundamentally redefines the scope of enterprise vulnerability management, Microsoft Corp. has issued updates addressing at least 570 security vulnerabilities across its Windows operating systems and enterprise software suite. The release nearly triples the previous record set by the software…

Read Full News