Solving the 2 a.m. Bottleneck: How a Peer-Reviewed RAG Framework is Transforming Incident Response

Executive Overview If you have ever been woken up at 2 a.m. by a cascading service degradation that you do not immediately recognize, you already understand the true bottleneck of modern incident response. It is rarely writing the code fix or executing the remediation script. Instead, the overwhelming majority of an on-call engineer’s time is…
Read Full News

Executive Overview: Navigating the Complex Currents of the Modern DevOps Job Market

In an era defined by rapid technological evolution and shifting macroeconomic tides, the demand for elite engineering talent remains one of the most critical barometers of enterprise health. To better serve our readership and provide actionable intelligence during these challenging economic times, DevOps.com is proud to introduce our weekly DevOps Jobs Report. This comprehensive initiative…

Read Full News

Beyond the Model: How Government Agencies Are Rewiring Infrastructure for the Era of Agentic AI

Executive Overview The conversation surrounding artificial intelligence within public sector operations has officially shifted. After years of iterative exploration—focused primarily on data aggregation, natural language processing, and isolated machine-learning pilots designed to streamline administrative workflows—government agencies are standing on the precipice of a profound technological evolution: agentic AI. Unlike conventional, single-task AI models that respond…

Read Full News

Critical Security Flaw Discovered in isolated-vm: The Hidden Dangers of Securing Untrusted JavaScript

Executive Overview For years, software developers working within the Node.js ecosystem have wrestled with one of computer science’s most persistent challenges: the safe and reliable execution of untrusted, user- or model-generated JavaScript code. Historically, developers relied heavily on vm2, an open-source Node.js library engineered to run untrusted scripts inside a simulated, isolated sandbox environment using…

Read Full News

The Great Engineering Bottleneck: How Tessl Code Review and "Standards-as-Code" Aim to Solve the Agentic Development Crisis

Executive Overview For decades, the primary bottleneck in software engineering was writing code. Developers spent hours manually building features, hunting down syntax errors, writing boilerplate logic, and managing tedious merges. Today, that paradigm has fundamentally inverted. The rise of autonomous coding agents—powered by advanced generative AI models—has unlocked unprecedented velocity. Development teams are no longer…

Read Full News

Beyond the Speed Trap: How KushoAI Rethink API Test Generation Through the Lens of Judgment

Executive Overview The initial wave of Large Language Model (LLM) adoption in software engineering promised a utopia of instantaneous productivity. For teams building and maintaining complex application programming interfaces (APIs), the arrival of generative AI tools offered the alluring prospect of automated test suite generation in mere seconds. Coverage breadth metrics spiked, development pipelines hummed…

Read Full News

The Resurrection of Software Engineering’s Most Maligned Methodology: Why "Waterfall 2.0" Is Taking Over the Age of LLMs

For the past two decades, the software engineering world has operated under an almost dogmatic consensus: Waterfall is dead. Killed off by the agility movement, the linear, heavily gated, documentation-heavy methodology of the late 20th century was widely cast aside as a relic of a slower era. Classic Waterfall—with its rigid phases of requirements gathering,…

Read Full News

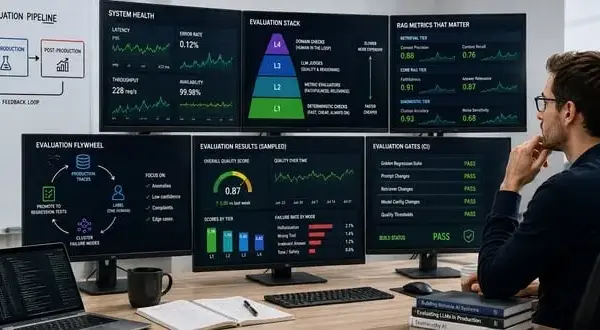
Beyond the Green Dashboard: Why Traditional SRE Fails AI and How to Build a Production-Grade Evaluation System

Executive Overview For the past fifteen years, Site Reliability Engineering (SRE) teams have relied on a dependable, time-tested playbook. Systems were deterministic. Given the same input, software produced the exact same output. Latency spikes, error rates, CPU throttles, and HTTP 5xx responses were all faithfully registered on dashboards rendered in reassuring shades of green. Today,…

Read Full News

Sophisticated Rust Supply-Chain Attack Weaponizes Core Ecosystem Utility, Showing Direct Ties to North Korean State-Sponsored Actors

Executive Overview In a chilling escalation of software supply-chain compromises, security researchers have uncovered a complex, highly coordinated, and lightning-fast cyberattack targeting the Rust programming language ecosystem. The operation compromised the maintainer account of arrayref—a foundational, low-level utility downloaded over 245 million times and present in roughly 75% of environments where Rust is deployed. The…

Read Full News

Dash0 Acquires Continuous Profiling Pioneer Polar Signals in Landmark OpenTelemetry Consolidation

Executive Overview In a strategic consolidation shaking up the modern observability and application performance monitoring (APM) markets, cloud-native observability startup Dash0 has officially announced the acquisition of Berlin-based continuous profiling specialist Polar Signals. The transaction—financial terms of which remain undisclosed—marks a significant milestone for Dash0, which was founded in 2023 and has rapidly scaled into…

Read Full News