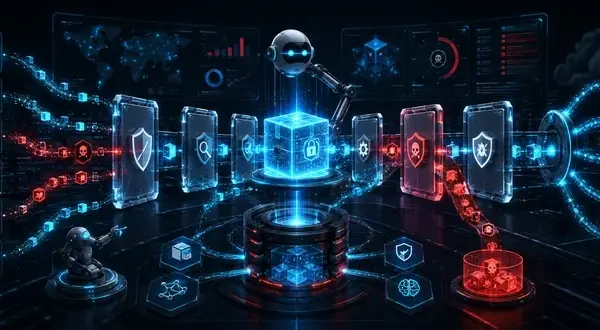
Securing the Autonomous SDLC: JFrog Unveils Zero-Touch Remediation and AI Agent Defense at swampUP 2026

Executive Overview As artificial intelligence rapidly transitions from a novelty assistive layer to an autonomous, active participant in the software development lifecycle (SDLC), the attack surface of the modern enterprise is undergoing a fundamental transformation. At its flagship swampUP 2026 conference, JFrog made a sweeping series of product announcements designed to address this seismic shift….
Read Full News

Securing the Build: How Advanced Risk Engineering, Analytics, and Data-Driven Safety Protect Construction Margins

By the Commercial Construction Desk Published: November 2024 Executive Overview In the high-stakes world of commercial construction, a catastrophic loss does more than damage physical assets—it can instantly vaporize project margins, trigger multi-party litigation, and delay closeout schedules for months. Yet, a widespread misconception persists across the industry: many contractors treat insurance as a passive…

Read Full News

Securing the Build: CrowdStrike’s Real-Time Shield Against the Next Generation of Software Supply Chain Attacks

Executive Overview The modern software supply chain has evolved into a high-stakes geopolitical and criminal battlefield. As organizations worldwide race to integrate artificial intelligence into their development pipelines, threat actors have found fertile ground in the vast, interconnected ecosystems of open-source libraries. At the annual Fal.con 2026 conference in Las Vegas, cybersecurity giant CrowdStrike made…

Read Full News

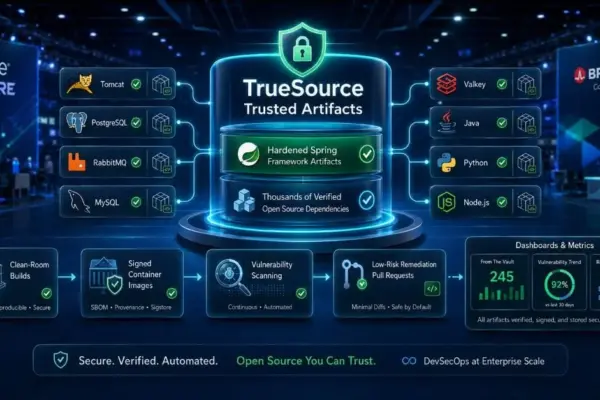
Securing the Enterprise Software Supply Chain: Broadcom Launches TrueSource at VMware Explore to Combat the AI-Driven Surge in Vulnerabilities

Executive Overview At the VMware Explore conference, Broadcom made a landmark announcement aimed at transforming how modern enterprises manage, secure, and deploy open-source software. The company unveiled TrueSource Trusted Artifacts by Broadcom, an expansive suite of hardened libraries and container images designed specifically for the widely used open-source Spring framework, along with the 5,000 vital…

Read Full News

Securing the AI Software Supply Chain: Why Trusted Open-Source Catalogs Are Replacing the Traditional Scanner

Executive Overview The paradigm of open-source software security is undergoing a structural collapse. For well over a decade, security operations teams, platform engineers, and developers have relied on a reactive, after-the-fact methodology: pulling a package from a public repository, running a static or dynamic vulnerability scanner, cross-referencing the results against Common Vulnerabilities and Exposures (CVE)…

Read Full News

Securing the Autonomous Frontier: AI Security Startup AIR Emerges From Stealth With $50 Million to Guard the Emerging Agent Supply Chain

Executive Overview As artificial intelligence rapidly transitions from a conversational novelty to an autonomous operational force within the enterprise, a hidden security crisis is quietly taking shape. Modern corporations are no longer just deploying chatbots; they are giving AI agents deep, functional access to internal databases, mission-critical enterprise systems, and the open internet. To achieve…

Read Full News

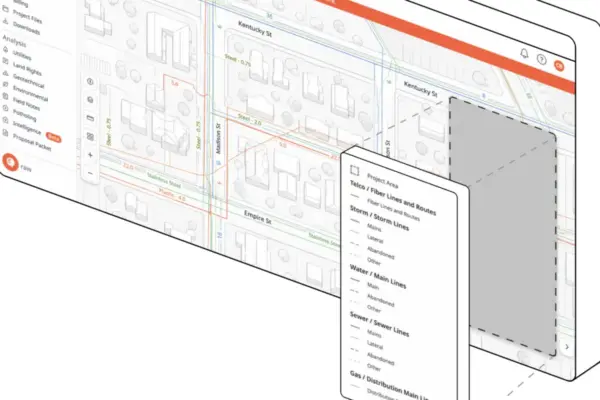
Mapping the Invisible Grid: How CivilGrid is Securing $26M to Solve America’s Underground Infrastructure Crisis

Executive Overview Every day, millions of people flick light switches, turn on faucets, and ignite gas stoves without giving a second thought to the sprawling, complex network of infrastructure humming quietly beneath their feet. Yet, this vital subterranean web—comprising thousands of miles of electric lines, gas pipes, water mains, and telecommunication cables—exists in a state…

Read Full News

Critical Security Flaw Discovered in isolated-vm: The Hidden Dangers of Securing Untrusted JavaScript

Executive Overview For years, software developers working within the Node.js ecosystem have wrestled with one of computer science’s most persistent challenges: the safe and reliable execution of untrusted, user- or model-generated JavaScript code. Historically, developers relied heavily on vm2, an open-source Node.js library engineered to run untrusted scripts inside a simulated, isolated sandbox environment using…

Read Full News

AI Chip Startup Etched Smashes Valuations, Securing $700 Million at a $21 Billion Valuation Led by Jane Street

Executive Overview In an era where artificial intelligence funding milestones are regularly rewritten, AI hardware startup Etched has defied traditional venture capital physics. On Tuesday, the company announced that it has successfully raised a staggering $700 million in a new financing round, catapulting its valuation to a breathtaking $21 billion. The funding round was led…

Read Full News

Securing the Software Supply Chain: The Rise of FIPS-Validated and STIG-Hardened Container Images in Regulated Industries

Executive Overview In the modern enterprise software lifecycle, security teams are no longer responsible solely for custom application code. They must account for every foundational layer, operating system dependency, cryptographic library, build provenance record, and inherited vulnerability introduced into a deployment via base images. For regulated software engineering teams—ranging from federal agencies and defense contractors…

Read Full News