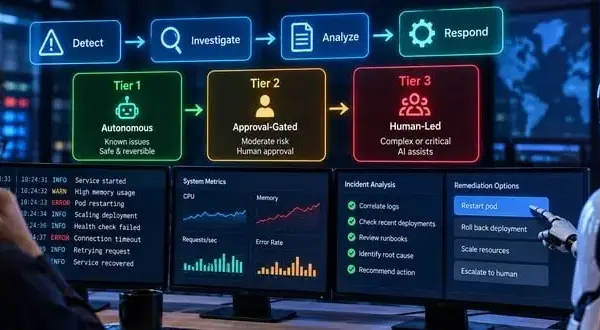
The Architecture of AI-Driven SRE: Implementing Tiered Autonomy in Incident Response

Executive Overview The role of Artificial Intelligence in Site Reliability Engineering (SRE) has undergone a fundamental transformation. No longer confined to the periphery as a read-only chatbot summarizing log files, AI agents are increasingly stepping into the shoes of operational teammates. Modern DevOps tooling—such as Aiden for SRE, the AWS DevOps Agent, and Azure DevOps…
Read Full News

Bridging the Divide: Why the Future of Managed Detection and Response Relies on Closed-Loop Offense and Defense

Executive Overview For decades, the cybersecurity industry has operated on a fractured premise: that offensive security—the art of breaking into systems to find flaws—and defensive operations—the 24/7 vigil of monitoring networks to keep intruders out—can function effectively in complete isolation from one another. Traditionally, red teams and penetration testers would drop into a corporate network,…

Read Full News

Bridging the Divide: Why the Future of Managed Detection and Response (MDR) Demands a Closed-Loop Offense-Defense Strategy

Executive Overview For over two decades, enterprise cybersecurity has operated on a foundational structural flaw: the strict organizational segregation of offensive and defensive teams. Traditionally, red teams and penetration testers were brought in to probe corporate networks, compile exhaustive static reports, and walk away—leaving behind a PDF of vulnerabilities that often gathered digital dust. Meanwhile,…

Read Full News

Solving the 2 a.m. Bottleneck: How a Peer-Reviewed RAG Framework is Transforming Incident Response

Executive Overview If you have ever been woken up at 2 a.m. by a cascading service degradation that you do not immediately recognize, you already understand the true bottleneck of modern incident response. It is rarely writing the code fix or executing the remediation script. Instead, the overwhelming majority of an on-call engineer’s time is…

Read Full News

Postmortem Analysis: Inside CISA’s Six-Month GitHub Secret Leak and Incident Response Failures

Executive Overview In an unprecedented move toward operational transparency, the Cybersecurity and Infrastructure Security Agency (CISA) has released a comprehensive postmortem detailing a severe, multi-month data leak caused by a third-party contractor. For nearly six months, an unencrypted public GitHub repository titled "Private CISA" hosted 844 megabytes of sensitive agency infrastructure data. The exposed records…

Read Full News

Navigating the Zero-Day Highway: Why Enterprise Architecture Dictates Incident Response Speed

Executive Overview When the next catastrophic zero-day vulnerability drops, an organization’s operational team will influence how quickly it reacts, but the ultimate outcome is decided long before disclosure—it is hardcoded into the enterprise architecture. Over the decades, organizations have accumulated sprawling portfolios of security technologies. Some detect attacks in progress, while others isolate workloads. Yet,…

Read Full News