Bridging the Divide: Why the Future of Managed Detection and Response Relies on Closed-Loop Offense and Defense
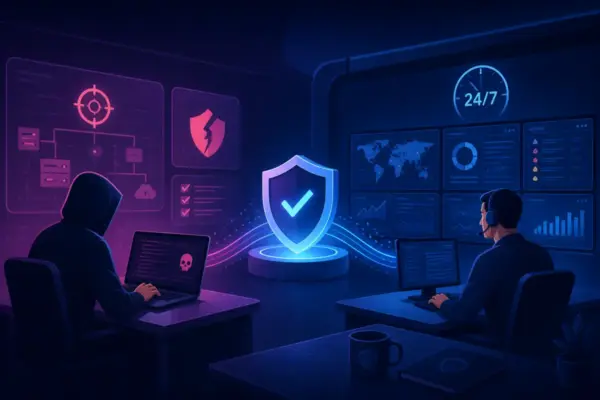
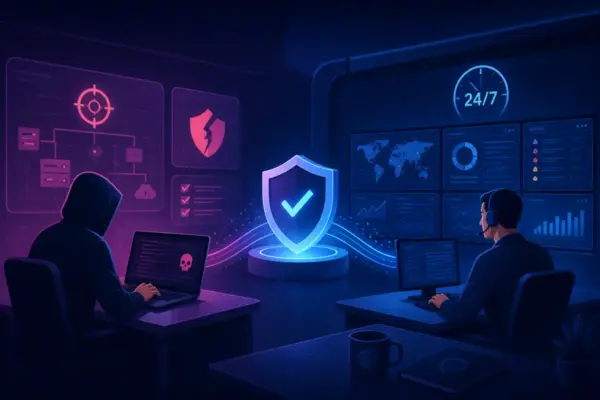
Executive Overview For decades, the cybersecurity industry has operated on a fractured premise: that offensive security—the art of breaking into systems to find flaws—and defensive operations—the 24/7 vigil of monitoring networks to keep intruders out—can function effectively in complete isolation from one another. Traditionally, red teams and penetration testers would drop into a corporate network,…