The AI Security Reckoning: IBM and Red Hat Uncover Over 400 Legacy Vulnerabilities, Exposing a Massive Open-Source Blind Spot

Executive Overview The landscape of enterprise software security is undergoing a profound and unsettling transformation. In a joint announcement that has sent ripples through the cybersecurity and software engineering communities, technology giants IBM and Red Hat revealed that their collaborative Lightwell initiative has successfully identified and remediated more than 400 previously unknown vulnerabilities within essential…
Read Full News

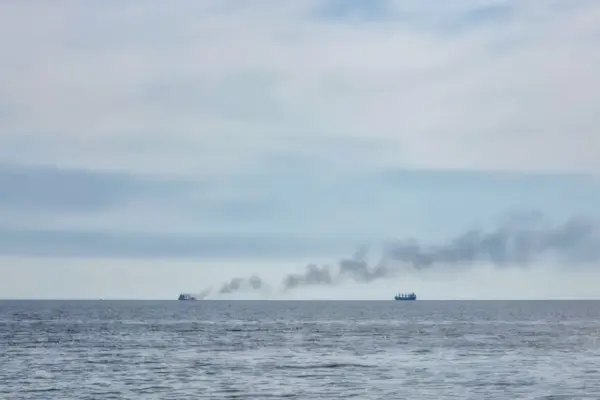
Black Sea Maritime Security Plunges Into Crisis: Unprecedented Drone Strikes Breach NATO Exclusive Economic Zones

By Global Security & Maritime Correspondent Published: October 2026 Executive Overview In what international security analysts are calling a dangerous and unprecedented escalation of the ongoing war in Eastern Europe, a coordinated series of sea and aerial drone attacks has struck commercial shipping within the exclusive economic zones (EEZs) of NATO member states. For the…

Read Full News

The Unpatched Reality: Why Enterprise Security’s Next Frontier is Operational Resilience, Not Just AI

Executive Overview For the better part of the past decade, the enterprise cybersecurity narrative has been dominated by a singular, obsessive focus: securing the software supply chain. Spurred by landmark industry crises such as SolarWinds, Log4Shell, and XZ Utils, organizations poured billions of dollars into fortifying their build pipelines, generating exhaustive Software Bills of Materials…

Read Full News

The AI Patch Surge: Microsoft Issues Record-Breaking 974 Security Fixes Amid Escalating Enterprise Strain

Executive Overview In an unprecedented event that highlights both the power of automated threat detection and the growing operational burden on IT departments, Microsoft Corp. released security updates addressing at least 974 security vulnerabilities across its Windows operating systems and ecosystem software. The massive release marks the single largest patch deployment in the history of…

Read Full News

The Paradigm Shift in Software Supply Chain Security: Why Gate-Based Enforcement and Edge-Native Policies Are Becoming Table Stakes

Executive Overview The software supply chain security ecosystem has reached a profound architectural inflection point. For over a decade, organizations operated under a reactive posture: dependencies were pulled into build environments on demand, scanned after installation, and flagged for vulnerabilities via traditional Common Vulnerabilities and Exposures (CVE) databases. Today, that model is obsolete. Accelerated by…

Read Full News

The Cost of Fractured Tech: How Hidden IT Sprawl Threatens Business Intelligence, Security, and Executive Decision-Making

Executive Overview Modern organizations pride themselves on being data-driven, yet a silent, systemic vulnerability is undermining executive decision-making across industries worldwide. When workplace information technology fragments across isolated departments, business intelligence integrity breaks down at its foundation. Disconnected tools create duplicate customer entries, force risky manual transfers between platforms, and produce conflicting figures for basic…

Read Full News

Navigating the Release-Day Crunch: How DevSecOps Integration Eradicates the Final Security Gate Bottleneck

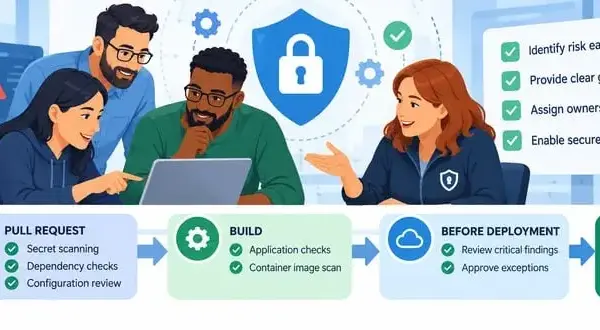
Executive Overview The scene is agonizingly familiar across software engineering organizations worldwide: mere hours before a major product release, a routine automated dependency scan flashes a critical warning. A newly flagged library vulnerability threatens to derail months of hard work. The development team scrambles to formulate a solution, only to realize that applying the immediate…

Read Full News

Security Researchers Uncover High-Risk GitLab Attack Vector Linked to Leaked Project Email Tokens

Executive Overview In the interconnected and fast-paced ecosystem of modern software development, security is frequently challenged by subtle design choices intended to maximize user convenience. A recent discovery by security researchers at Aikido Security has brought this ongoing tension into sharp focus, exposing a security concern within GitLab’s incoming email handling. According to findings detailed…

Read Full News

Autonomous Software Development at Scale: Blitzy Launches Free Sandbox to Help DevOps Teams Win the AI Security Race

Executive Overview The landscape of software development and security is undergoing a seismic, irreversible shift. As malicious actors increasingly leverage generative artificial intelligence to unearth zero-day exploits, map legacy infrastructures, and automate cyberattacks at unprecedented velocities, enterprise development teams find themselves locked in an asymmetric race against time. To level the playing field, Blitzy—a pioneering…

Read Full News

Meta’s "Security-First" AI Agent, Muse, Rocked by Critical Zero-Day Vulnerability

Executive Overview Meta founder and CEO Mark Zuckerberg has spent months championing the architecture of Muse, the company’s flagship macOS AI assistant. Pithed as a revolutionary leap forward in automated personal productivity, Zuckerberg and Meta’s engineering teams aggressively marketed the agent as being "built from the ground up for privacy and security." Promoted as an…

Read Full News