The Paradigm Shift in Software Supply Chain Security: Why Gate-Based Enforcement and Edge-Native Policies Are Becoming Table Stakes
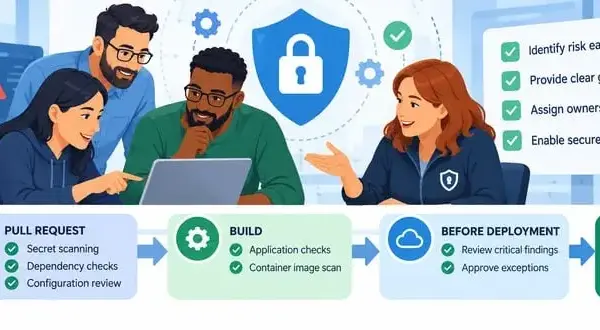
Executive Overview The software supply chain security ecosystem has reached a profound architectural inflection point. For over a decade, organizations operated under a reactive posture: dependencies were pulled into build environments on demand, scanned after installation, and flagged for vulnerabilities via traditional Common Vulnerabilities and Exposures (CVE) databases. Today, that model is obsolete. Accelerated by…