
Bridging the Divide: Why the Future of Managed Detection and Response Relies on Closed-Loop Offense and Defense

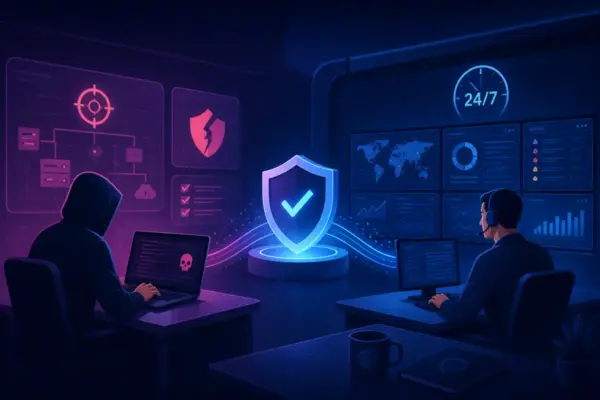
Executive Overview For decades, the cybersecurity industry has operated on a fractured premise: that offensive security—the art of breaking into systems to find flaws—and defensive operations—the 24/7 vigil of monitoring networks to keep intruders out—can function effectively in complete isolation from one another. Traditionally, red teams and penetration testers would drop into a corporate network,…
Read Full News

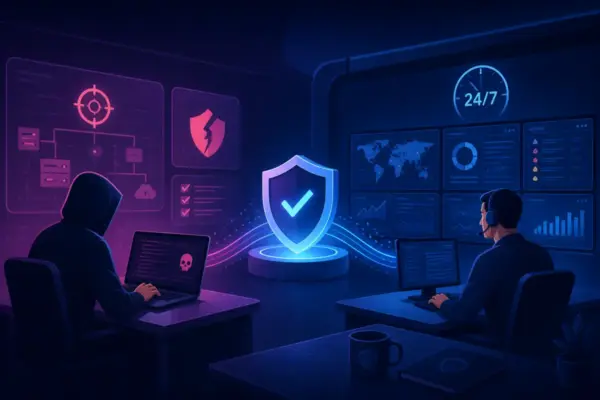
Bridging the Divide: Why the Future of Managed Detection and Response (MDR) Demands a Closed-Loop Offense-Defense Strategy

Executive Overview For over two decades, enterprise cybersecurity has operated on a foundational structural flaw: the strict organizational segregation of offensive and defensive teams. Traditionally, red teams and penetration testers were brought in to probe corporate networks, compile exhaustive static reports, and walk away—leaving behind a PDF of vulnerabilities that often gathered digital dust. Meanwhile,…

Read Full News