
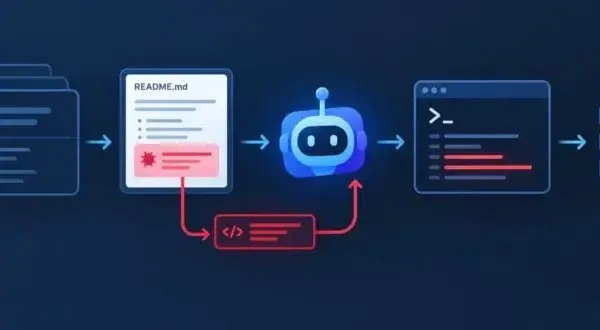
The Trojan Horse in the Terminal: How AI Coding Agents Expand the Software Supply Chain Attack Surface Beyond the Sandbox

Executive Overview The rapid integration of generative artificial intelligence into everyday software engineering has fundamentally altered how code is written, curated, and deployed. Developers routinely enlist AI coding agents to automate tedious workflows—searching GitHub for libraries, configuring project architectures, diagnosing installation snags, and initializing new developer tools. These autonomous or semi-autonomous systems can query codebases,…
Read Full News

Inside the Takedown of TeamPCP: How Law Enforcement Unmasked the Masterminds Behind the Largest Software Supply Chain Attack Spree

Executive Overview In a milestone international law enforcement operation, the Australian Federal Police (AFP), working in close coordination with the Federal Bureau of Investigation (FBI) and the Western Australia Police Force (WAPF), has dismantled the primary operational core of TeamPCP. The prolific cybercrime and data extortion syndicate is widely credited with engineering the longest-running, most…

Read Full News

Sophisticated Rust Supply-Chain Attack Weaponizes Core Ecosystem Utility, Showing Direct Ties to North Korean State-Sponsored Actors

Executive Overview In a chilling escalation of software supply-chain compromises, security researchers have uncovered a complex, highly coordinated, and lightning-fast cyberattack targeting the Rust programming language ecosystem. The operation compromised the maintainer account of arrayref—a foundational, low-level utility downloaded over 245 million times and present in roughly 75% of environments where Rust is deployed. The…

Read Full News

Unfixable Architecture: The Fundamental Flaw Leaving Large Language Models Vulnerably Open to Attack

Executive Overview As artificial intelligence rapidly transitions from an experimental novelty into the hidden operating system of global infrastructure—embedded deeply within military command rooms, healthcare systems, online shopping engines, and financial institutions—a sobering realization has emerged from the cutting edge of machine learning research. According to a landmark paper presented at the International Conference on…

Read Full News

Massive "Shai-Hulud" npm Supply-Chain Attack Compromises Over 1,280 Packages and 2 Billion Monthly Installs

Executive Overview The global software development ecosystem is grappling with one of the most aggressive and fast-moving supply-chain attacks in recent memory. Cybersecurity researchers from Aikido Security and Endor Labs have sounded the alarm over a rapidly spreading malware campaign linked to the notorious "Shai-Hulud" threat group. This sophisticated worm has successfully compromised well over…

Read Full News