Microsoft Issues Record-Breaking 974 Security Patches in Historic September Release as AI Accelerates Vulnerability Discovery

Executive Overview In an unprecedented expansion of its monthly maintenance cycle, Microsoft Corp. has issued security updates to resolve a staggering 974 security vulnerabilities across its Windows operating systems and associated enterprise software suite. The September 2026 Patch Tuesday updates mark the single largest patch release in the software giant’s history, highlighting a transformative shift…
Read Full News

Deciphering the Adtech Shadow Supply Chain: How DecryptAds Exposes Foreign Surveillance, Malvertising, and Data Exploitation

Executive Overview In the modern programmatic advertising landscape, the infrastructure powering web and mobile banner ads has evolved into a vast, opaque network of real-time bidding platforms, data brokers, and intermediary resellers. While designed to automate online ad sales, this complex web quietly harvest personal data, tracks user movements, and facilitates cyber threats. Determining which…

Read Full News

Mastermind Behind Mass Snowflake Cloud Extortions Pleads Guilty in Landmark Cybercrime Case

Executive Overview In one of the most significant judicial developments in recent cybersecurity history, 26-year-old Canadian national Connor Riley Moucka—recognized by federal authorities and threat intelligence researchers as one of the most prolific cybercrime threat actors of 2024—has formally pleaded guilty in U.S. federal court. Moucka, a resident of Kitchener, Ontario, admitted to multiple counts…

Read Full News

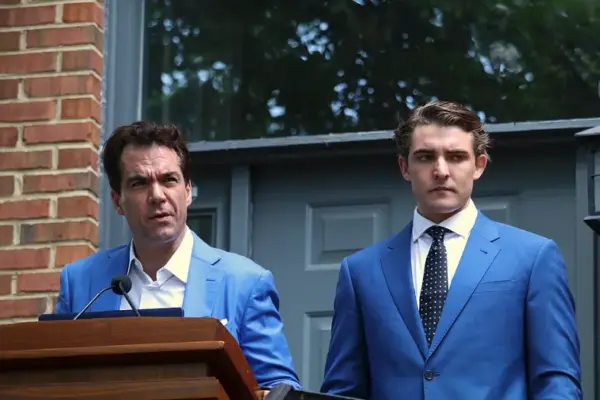
Shadowy Zero-Day Brokerage Linked to Notorious Conspiracy Theorists and Convicted Felons

Executive Overview: Convicted Felons Pivot to Offensive Cyber Capabilities A shadowy cybersecurity startup offering millions of dollars to purchase zero-day software vulnerabilities has been uncovered as the latest venture of Jack Burkman and Jacob Wohl—a pair of far-right conspiracy theorists, disgraced political operatives, and convicted felons. Operating under the name IRIS C2 and backed by…

Read Full News

Anatomy of a Federal Secret Leak: CISA Postmortem Reveals Six Months of Exposed AWS GovCloud Keys and Operational Blindspots

Executive Overview In an extraordinary act of institutional transparency, the Cybersecurity and Infrastructure Security Agency (CISA)—the United States’ primary federal defense agency tasked with safeguarding critical infrastructure and federal civilian networks—has published a comprehensive incident postmortem detailing a significant internal data leak. The security breach stemmed from a third-party contractor who unwittingly published a public…

Read Full News

The AI Vulnerability Tsunami: Microsoft Issues Record-Breaking 570 Security Fixes in Unprecedented Patch Tuesday

Executive Overview In what marks an unprecedented watershed moment for software security, Microsoft Corp. has released a massive security update addressing at least 570 vulnerabilities across its Windows operating systems and broader software portfolio. This update nearly triples the software giant’s previous record-breaking Patch Tuesday release, signaling a fundamental transformation in how security flaws are…

Read Full News

Unmasking TeamPCP: Inside the Law Enforcement Takedown of the World’s Most Prolific Supply Chain Hacking Syndicate

Executive Overview In a coordinated law enforcement operation spanning multiple continents, federal authorities in Australia, supported by the Federal Bureau of Investigation (FBI), have dismantled the core operational command of TeamPCP—a notorious cybercrime and data extortion collective responsible for the longest-running and most destructive software supply chain attack campaign in digital history. The Australian Federal…

Read Full News

Living Room Botnets: LG Moves to Purge Residential Proxy SDKs from webOS Ecosystem

Executive Overview In a significant shift regarding smart TV security and platform governance, LG Electronics USA has announced a comprehensive crackdown on software applications within its webOS store that secretly convert televisions into active, always-on residential proxy nodes. The decision follows alarming revelations by cybersecurity research firm Spur, which discovered that over 42 percent of…

Read Full News

The Invisible Ad-Fraud Empire Inside Budget Streaming TV Boxes

Executive Overview For years, cybersecurity researchers and federal law enforcement agencies have warned consumers about the hidden dangers lurking inside unbranded, off-brand streaming television boxes. Promoted across major online marketplaces and by social media influencers as "all-in-one" entertainment solutions that promise access to premium channels and subscription streaming services for a modest one-time fee, these…

Read Full News

The AI-Driven Patch Deluge: Microsoft Unveils 398 Security Fixes Amid Industry-Wide Vulnerability Surge

Executive Overview In an era increasingly defined by AI-augmented vulnerability research, Microsoft has issued a massive security update addressing at least 398 security flaws across its Windows operating systems and supported software ecosystem. Released as part of its August 2026 Patch Tuesday deployment, the update highlights a broader paradigm shift: enterprise defenders are now facing…

Read Full News