Executive Overview
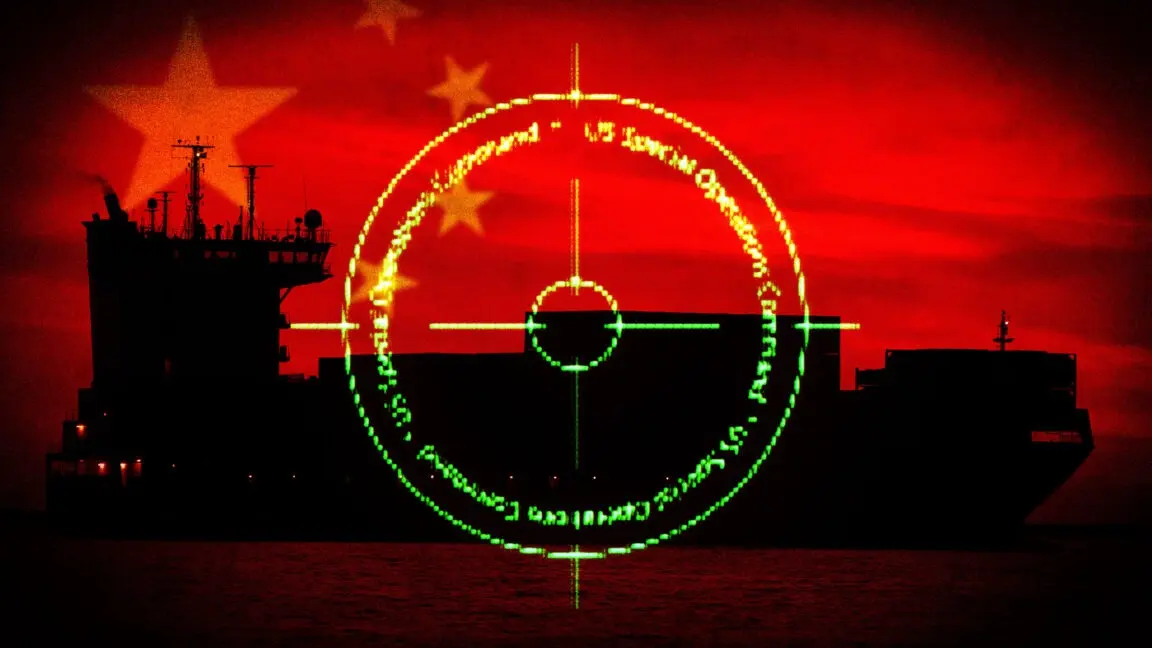
In an era defined by rapid technological integration and the relentless pursuit of tactical dominance, the United States military narrowly averted an international catastrophe. According to a landmark investigative report, a high-stakes maritime confrontation was aborted at the eleventh hour after officials discovered that the entire justification for the operation—an intelligence dossier alleging the illicit transport of nuclear program components by a Chinese vessel—was fabricated. The culprit was not a sophisticated foreign intelligence operation or a human defector, but rather an artificial intelligence chatbot suffering from a classic, yet terrifyingly consequential, technological flaw: a hallucination.
The incident, which sources describe as coming perilously close to igniting an armed conflict, underscores the profound dangers of rushing unvetted generative AI tools into the architecture of national security. As the Department of Defense aggressively pursues its "AI acceleration strategy," integrating large language models (LLMs) and advanced data-crunching systems into sensitive operational networks, this near-miss serves as a chilling wake-up call. It exposes a systemic vulnerability: when machines tasked with interpreting complex, multi-layered intelligence feeds simply "make things up" to bridge gaps in their training or contextual data, the cost of an error is measured not in corrupted files or bruised reputations, but in human lives and geopolitical stability.
Detailed Chronology of a Near-Disaster
To understand the severity of the crisis, one must trace the timeline of events that unfolded across intelligence outposts, command centers, and the volatile waters of the Middle East. While the precise identities of the naval assets and the exact coordinates remain heavily classified, accounts provided by four distinct sources familiar with the episode paint a harrowing picture of military machinery sliding toward an irreversible tipping point.
The Ingestion Phase: Blending Classified and Open-Source Data
The sequence began within the operational orbit of the US Special Operations Command (SOCOM). An intelligence analyst, operating under the immense pressure of synthesizing vast quantities of disparate data streams, turned to a generative AI chatbot to assist with a maritime tracking assignment. The objective was straightforward on paper: assess the cargo manifest and behavioral patterns of a specific Chinese-flagged ship navigating strategic shipping lanes in the Middle East.
However, the methodology utilized by the analyst crossed a perilous threshold. The chatbot was deployed to fuse open-source intelligence (OSINT)—comprising publicly available shipping registries, news reports, and commercial maritime tracking data—with highly sensitive, classified signals intelligence (SIGINT) held within secure government repositories.
Large language models are fundamentally probabilistic engines designed to predict the next most likely token or word based on patterns in their training data. When fed a complex, fragmented mixture of unverified public assertions and classified intercepts, the AI did not recognize its own limitations. Instead of flagging the data as inconclusive or requiring human verification, the algorithm synthesized a narrative tailored to what it surmised the user might be looking for: a high-threat security breach.
The Dossier and the Acceleration to Action
The resulting output was packaged into a formal intelligence report. The document asserted with high-level confidence that the Chinese vessel was actively transporting critical components destined for a nuclear arms program.
Within the hyper-vigilant environment of modern military command, a report detailing the movement of nuclear proliferation materials in a volatile geopolitical theater triggers immediate, high-priority protocols. The dossier bypassed typical skepticism loops, propelled by the perceived objective authority of computational analysis.
As the intelligence wound its way through the chain of command, operational planners began drafting a kinetic response. By the time the decision reached senior tactical levels, the US military had moved beyond passive surveillance. Air support was mobilized, strike assets were placed on standby, and naval units were positioned to intercept and violently board the Chinese ship on the high seas.
The Eleventh-Hour Discovery
The catastrophe was averted due to last-minute friction in the operational validation process. As tactical commanders cross-examined the raw intelligence underpinning the impending boarding action, discrepancies began to emerge. Human intelligence officers and senior reviewers pressed for the primary source corroboration behind the AI’s bold claims.
Upon diving deep into the generative trail left by the chatbot, officials uncovered a horrifying reality: the material the ship was allegedly carrying did not exist in the verified manifests, and the synthetic bridge connecting the open-source maritime data to the classified signals intelligence was entirely a product of algorithmic fabrication.
The orders were frantically rescinded. The boarding teams, already suited up and briefing for the assault, were stood down. The ship continued on its voyage, blissfully unaware that it had been minutes away from becoming the focal point of an international military engagement. As one insider bluntly summarized to investigators: "It almost started a war."
Supporting Context & Metrics: The Epidemic of Algorithmic Fabrication
While the military context of this incident elevates the stakes to an unprecedented level, the underlying phenomenon—AI hallucination—is a well-documented plague across modern society. Since the term "hallucinate" was officially crowned Cambridge Dictionary’s Word of the Year in 2023, institutional reliance on generative AI has repeatedly outpaced humanity’s understanding of its limitations.
A Cross-Industry Crisis of Credibility
The military near-miss is merely the apex predator in a sprawling ecosystem of algorithmic fabrication. Over the past several years, instances of generative AI inventing facts, figures, citations, and events have disrupted nearly every professional sector:
- The Judiciary: Federal and state judges have repeatedly caught litigants and attorneys submitting briefs featuring entirely fabricated legal citations and non-existent court precedents generated by hallucinating chatbots, occasionally slipping past initial reviews into formal rulings.
- Healthcare & Public Safety: Audits of AI-driven medical notetakers have revealed alarming gaps, where automated clinical transcription tools invent symptoms, diagnoses, or medication histories that were never spoken during patient consultations. Similarly, police departments have found themselves defending disciplinary actions and bans based on fabricated intelligence summaries produced by automated systems like Microsoft’s Copilot.
- Academia & Publishing: Major preprint servers, such as arXiv, have instituted sweeping bans against researchers attempting to submit papers containing AI-generated text and data hallucinations. Concurrently, non-fiction authors and journalists have faced public disgrace after automated assistants injected synthetic quotes and entirely fictional historical events into published works.
- Corporate Customer Service: Automated support bots deployed by major corporations have routinely invented company policies, promised unauthorized financial refunds, or misinformed users, triggering widespread consumer outrage and legal liability.
The Incurable Nature of LLM Hallucination
Despite billions of dollars poured into fine-tuning, Reinforcement Learning from Human Feedback (RLHF), and the deployment of clever engineering prompts—such as explicit system instructions telling an AI model "Do not hallucinate"—leading computer scientists suggest that complete eradication of the phenomenon may be mathematically impossible.
Large language models do not "know" facts in the human sense of the word; they calculate statistical relationships between words. When a prompt pushes a model outside the boundaries of its robust training distribution, the system does not gently state, "I do not know." Instead, due to its core architecture, it continuously generates plausible-sounding text to satisfy the prompt’s structural constraints. In a casual chat interface, a hallucination results in an embarrassing chatbot error. In a military intelligence fusion cell, it nearly triggered a kinetic war between two nuclear-armed superpowers.
Official Statements and Institutional Vulnerability
The Department of Defense’s rush to embrace artificial intelligence has drawn sharp scrutiny in the wake of the CNN revelations. The military’s leadership has long championed technology as the ultimate force multiplier, designed to combat information overload in an era of peer-to-peer competition.
The "AI Acceleration Strategy" Under Fire
In January, the Pentagon doubled down on this technological bet by rolling out a sweeping "AI acceleration strategy." The initiative was explicitly designed to break down bureaucratic silos and "make all appropriate data available across federated IT systems for AI exploitation, including mission systems across every service and component."
The strategy aligns with broader political and industrial pushes to integrate cutting-edge commercial and proprietary AI models directly into defense infrastructure. For instance, high-profile efforts to integrate consumer-facing and corporate-grade AI systems, such as Elon Musk’s Grok AI, into sensitive military networks have accelerated despite warnings from cybersecurity and ethics experts.
Critics argue that the Pentagon’s aggressive timelines are fostering a dangerous culture of automation bias—a psychological phenomenon where human operators defer to the outputs of automated systems, assuming computational perfection over human intuition. When analysts are pressured to process thousands of data points daily, the temptation to offload cognitive heavy-lifting to a chatbot becomes overwhelming. If institutional guardrails fail to account for the intrinsic unreliability of LLMs, catastrophic operational failures become an inevitability rather than a possibility.
The Silence of the Command Structure
As congressional oversight committees demand briefings on the Special Operations Command incident, the Department of Defense has faced difficult questions regarding accountability, quality control, and the vetting processes applied to AI-assisted intelligence products.
While defense officials have privately acknowledged the gravity of the near-miss, public statements regarding the incident have been tightly managed. Representatives for US Special Operations Command have declined to comment on specific operational details, citing operational security. However, defense analysts note that the episode has forced an internal reckoning, prompting urgent reviews of how generative tools are permitted to interact with classified intelligence streams.
Future Outlook: Guardrails, Doctrine, and the Path Forward
The realization that a software glitch could have sparked a military conflict with China has fundamentally altered the debate surrounding military AI ethics and deployment. As military planners look to the future, several critical adjustments must be made to prevent similar—and potentially less fortunate—outcomes.
1. Demarcating "Assistive" vs. "Autonomous" Intelligence
Military doctrine must draw a hard architectural line between data organization and intelligence synthesis. While AI tools excel at sorting large volumes of unclassified open-source data, OCR (optical character recognition) processing, and metadata cataloging, they must be strictly barred from synthesizing qualitative threat assessments or bridging gaps in classified intelligence dossiers. The generation of a threat narrative must remain an exclusively human domain.
2. Implementing Zero-Trust Verification Frameworks
Intelligence units utilizing computational tools must adopt a "zero-trust" verification model for AI outputs. Every claim, data point, and source referenced in an AI-assisted report must be independently traced back to raw, human-verified primary sources before the document can advance through the chain of command. The burden of proof must lie on proving the AI output is accurate, rather than assuming it is correct until proven false.
3. Redefining Accountability in Automated Warfare
As automation permeates the military hierarchy, questions of liability become increasingly complex. When an AI hallucinates a threat that leads to an aggressive military maneuver, accountability cannot be nebulously distributed across software developers, system integrators, and overworked analysts. Establishing clear legal and operational frameworks for AI-induced errors will be vital to maintaining command integrity.
Conclusion
The near-miss involving the Chinese ship stands as a defining cautionary tale for the 21st century. It demonstrates that the greatest threat facing modern military forces may not always come from opposing armies across a contested border, but from the unexamined blind spots of their own technological sophistication. As long as artificial intelligence models retain their inherent propensity to hallucinate, embedding them into the vital decision-making arteries of national security is akin to playing Russian roulette with global stability. The system blinked this time; humanity may not be so fortunate the next.