Pentagon Data Breach Exposes Records of 2.8 Million Service Members in Massive Cyber Incident

WASHINGTON — In one of the most sweeping security failures in the history of the United States Department of Defense, the Pentagon has begun formally notifying more than 2.8 million current and former military personnel that their highly sensitive personal records were stolen during a months-long, unauthorized compromise of a core departmental network. The breach,…
Read Full News

The Evolution of ClickFix: How Social Engineering and the Terminal Bypass Modern Cyber Defenses

Executive Overview The landscape of cybercrime is undergoing a profound and troubling paradigm shift. For decades, the dominant vector for malware delivery relied on technical exploits, complex software vulnerabilities, or heavy infrastructure investments designed to trick operating systems into trusting malicious code. Threat actors spent millions of dollars—or dedicated months of labor—acquiring stolen Microsoft-trusted signing…

Read Full News

Inside CISA’s Six-Month Credential Exposure: Lessons from the Cyber Agency’s Landmark Postmortem

Executive Overview In an unprecedented display of public accountability, the Cybersecurity and Infrastructure Security Agency (CISA)—the United States’ lead federal authority on cybersecurity and critical infrastructure protection—has released a comprehensive postmortem detailing a significant internal security lapse. For nearly six months, an unencrypted public GitHub repository maintained by a third-party contractor exposed administrative credentials, internal…

Read Full News

State-Sponsored Cyber Espionage: The Anatomy of the "BlueMoon" Exploit Kit and the New Era of AI-Driven Zero-Day Exploitation

Executive Overview In the continuously evolving landscape of modern cybersecurity, a significant paradigm shift has been uncovered. Security researchers at enterprise cybersecurity firm Proofpoint have exposed a sophisticated, highly collaborative threat campaign utilizing a standardized, nearly identical exploit kit known as BlueMoon. This potent toolset actively targets critical vulnerabilities across Chromium-based web browsers and legacy-to-moderate…

Read Full News

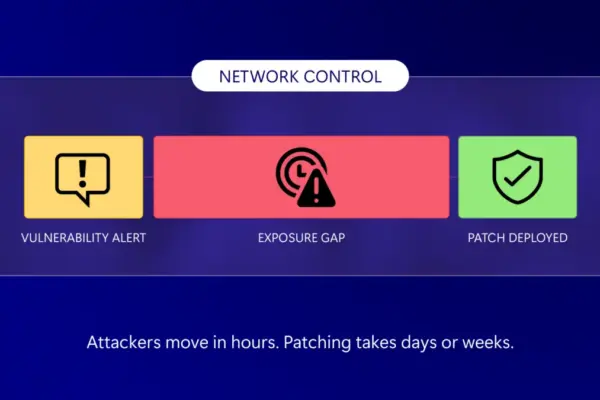
The Collapse of the Patch Window: How AI and Cloud Complexity Are Forcing a Revolution in Cyber Defense

Executive Overview For nearly three decades, corporate cybersecurity strategies have rested on a predictable foundation: a vulnerability is identified, a Common Vulnerabilities and Exposures (CVE) identifier is assigned, security operations teams assess their risk, patches are verified in staging environments, and code updates are deployed to production before adversaries can execute exploits at scale. That…

Read Full News

Unprecedented Cyber Breach: Dark Web Bazaars Flood with 153 Million Driver’s Licenses Linked to Identity Provider Verification Flaws

Executive Overview In what is shaping up to be one of the most severe enterprise supply-chain compromises of the decade, a newly established dark web identity theft marketplace dubbed Nexus has begun offering digital scans of state-issued driver’s licenses and official identification documents belonging to more than 153 million North Americans. Operating across major cybercrime…

Read Full News

The New Frontier of Endpoint Compromise: Lunar Cyber Launches Token Exposure Monitoring to Combat the Rise of Machine Identity Theft

Executive Overview The landscape of cybersecurity is undergoing a radical shift, moving away from simple credential harvesting toward the sophisticated extraction of non-human identities (NHIs). As software development grows increasingly automated and reliant on cloud-native architectures, artificial intelligence, and distributed services, the keys to the digital kingdom are no longer just human-facing passwords. They are…

Read Full News

The Anatomy of a Zero-Day Charade: How Two Notorious Conspiracists Rebranded as Offensive Cyber Brokers

Executive Overview A newly emerged cybersecurity venture promising multi-million-dollar bounties for zero-day software exploits has been identified as the latest front operation engineered by two of America’s most prolific political disinformation artists and convicted felons. Operating under the brand IRIS C2 and registered corporately as Calvexa Group LLC, the firm claims to procure high-tier cyber-weapons…

Read Full News

Unmasking the Invisible Tracker: How DecryptAds Exposes the Hidden Cyber Risks of Modern Adtech

Executive Overview For over two decades, the global digital advertising ecosystem has operated behind an opaque curtain. While millions of web users interact daily with mainstream news outlets, streaming services, and mobile applications, a labyrinthine infrastructure of data brokers, supply-side platforms (SSPs), and ad exchanges silently tracks user behavior, harvests sensitive telemetry, and executes real-time…

Read Full News

Urgent Cyber Threat Alert: Active Exploitation of macOS Screen Sharing Vulnerability (CVE-2026-65400) Triggers Global Security Warnings

Executive Overview In the rapidly evolving landscape of modern cybersecurity, zero-day and newly disclosed vulnerabilities frequently transition from academic curiosity to active weaponization within a matter of days—or even hours. This harsh reality has once again been underscored by urgent warnings issued by international cybersecurity authorities regarding a high-severity remote code execution (RCE) vulnerability impacting…

Read Full News